Keryn HeadlinesDaily, Wednesday 18 November 2026 · No. 2 · Covers 17 November 2026 00:00 to 18 November 2026 00:00 UTC |
From the editorIf you install Microsoft's PyPI package agent-framework, check locked and installed versions for 1.26.1 and 1.26.2 2. Wiz reports both versions shipped with an added credential stealer on November 17, 2026 at 20:35 UTC, and now sit in quarantine 2. The package gets almost 200k downloads a month, and Wiz's headline names Azure and CI pipelines as targets 2. Wiz's excerpt does not list which credentials the stealer takes 2. Our advice is to rotate any secret an environment running either version could reach. If you build or run Java services on OpenJDK, track CVE-2026-114938, a remote code execution flaw Datadog calls Java4Shell 1. Datadog's excerpt names no affected versions or fix 1. We suggest you inventory OpenJDK use and watch for fixes. If your coding agents sign in through device code flow, note that Microsoft presents this as lab research, not a reported attack 6. Microsoft shows how device code phishing can extend to AI coding agents, using GitHub Copilot CLI as an example 6. We suggest you review which agents accept device codes. AI-drafted. Not reviewed by a human editor: it passed automated checks only. Published by Keryn. Corrections: keryn@keryn.dev |
Top developments |
 Java4Shell: Remote Code Execution in OpenJDK (CVE-2026-114938)Why it matters: A remote code execution flaw dubbed Java4Shell (CVE-2026-114938) in OpenJDK may affect any Java-based service your team builds or runs, so check whether you use OpenJDK and watch for fixes. Datadog · Advisory · Remediation Builds (CVE-2026-114938, from vendor records): fixed in Amazon Corretto 27 27.0.1.1.4, Red Hat Build of OpenJDK 17.0.21.1 , Red Hat Build of OpenJDK 21.0.13.1 , Red Hat Build of OpenJDK 25.0.5.1 , Temurin Build of OpenJDK 25.0.5.1 ; affected, no fix stated: Red Hat build of Keycloak. |
 Microsoft agent-framework Compromised: Credential Stealer Targets Azure and CI PipelinesWiz · Incident · SCA |
 Optimizely supply chain attack served malware on CNN, Fox News, BBC sitesWhy it matters: A suspected compromise of Optimizely led to malicious JavaScript loading on many major sites, so teams embedding third-party scripts should review those dependencies now for signs of tampering. BleepingComputer · Incident · SCA |
 N-able Patches 17 N-central Flaws as Attackers Exploit Earlier Bugs to Deploy Crypto MinersWhy it matters: N-able's N-central 2026.4 Hotfix 3 is described as a critical security update, and attackers are reportedly exploiting earlier bugs to deploy crypto miners, so teams running this RMM platform should patch promptly. The Hacker News · Advisory · Remediation |
 Cloud keys leaked in Docker Hub images are stolen within secondsBleepingComputer · Research · SCA |
Agentic SDLC |
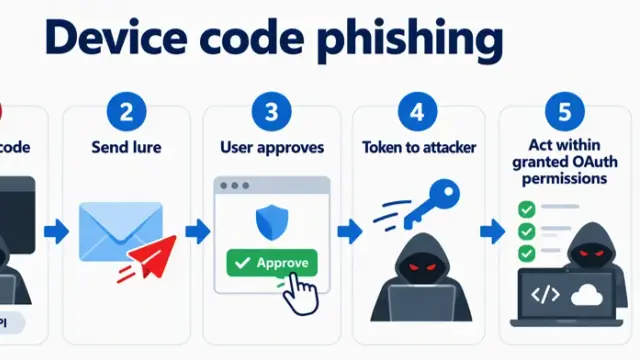 The risks of device code authentication for AI coding agentsWhy it matters: Device code phishing can be extended to AI coding agents such as GitHub Copilot CLI, so a single approved sign-in code can give attackers access; teams should review how agents authenticate. Microsoft · Research · Agentic SDLC, AI Security |
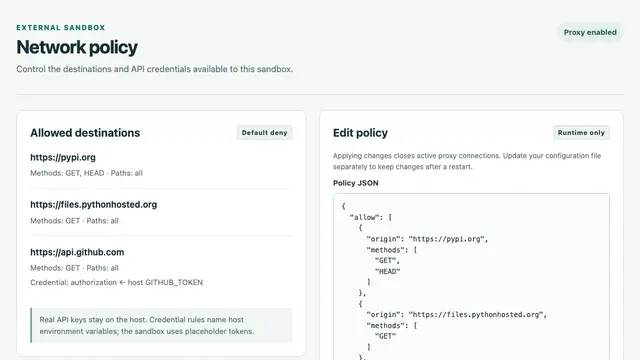 External sandboxes for coding agentsSimon Willison · Release · Agentic SDLC, AI Security |
Remediation |
Exploited Before It Was Fixed? Vulnerability Timelines from Open, Machine-Readable EvidencearXiv · Research · Remediation |
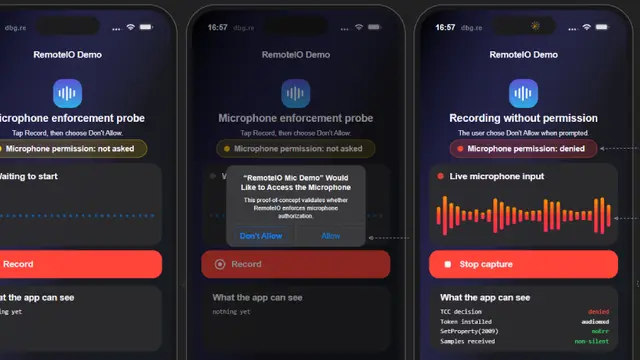 Researchers Detail iPhone Flaw That Let Apps Record Audio Despite Denied Microphone PermissionThe Hacker News · Research · Remediation |
Models |
SEAM: Computer-Use Agents Know the Harm Between Screens, and Commit It AnywayarXiv · Research · Models |
Who Pays for Byzantine Robustness? Validity, Data-Share Dictatorships, and Fairness When Only a Few Hospitals CollaboratearXiv · Research · Models |
Is 4-Bit Quantization More Than Noise to a Chat Model's Safety Behaviour? Attributing Behavioural Shifts with Matched PerturbationsarXiv · Research · Models |
AI Security |
Network-Exposed Configuration Attacks on LLM-Controlled Social RobotsarXiv · Research · AI Security |
GapLeak: When Privacy-Preserving LLM-based Web Agents Become a Privacy RiskarXiv · Research · AI Security |
Can You Undo It? Reversibility Classes for AI Agent ActionsarXiv · Research · AI Security |
Advisories in this window
|
Titles, links and short excerpts only; every item links to its source. Selection is automatic; the editor's note is AI-drafted and checked as described. Preview: the unsubscribe link and Keryn's postal address are added to each email when it is sent. |