Advisories
The full advisory stream, one row each: package advisories and vulnerability notices. In the main feed they are grouped into bulletins by ecosystem and day. Each advisory is independent; a bulletin is not a campaign.
- 8 last 24h
- 794 last 7 days
- 947 in view
- RSS
GHSA-6crj-9fxx-v653: Malware in @leadstack/crm-connect
@leadstack/crm-connect = 1.0.15 → remove it
Why tagged?
- SCA from the title:
GHSA-6crj-9fxx-v653: Malware
- SCA from the title:
GHSA-hqfp-fhqg-4xc5: Malicious code in @leadstack/crm-connect (npm)
@leadstack/crm-connect = 1.0.15 → remove it | = 1.0.20 → remove it | = 1.0.30 → remove it | = 1.0.21 → remove it | = 1.0.19 → remove it | = 1.0.18 → remove it
Why tagged?
- SCA from the title:
GHSA-hqfp-fhqg-4xc5: Maliciou
- SCA from the title:
GHSA-p7r2-5ppv-hr6g: Malicious code in @c1-ease/core (npm)
@c1-ease/core = 3.0.0 → remove it | = 2.0.0 → remove it | = 1.0.0 → remove it | = 1.0.1 → remove it | = 99.0.1 → remove it | = 2.0.1 → remove it; +1 more
Why tagged?
- SCA from the title:
GHSA-p7r2-5ppv-hr6g: Maliciou
- SCA from the title:
GHSA-q599-9j7q-8xf5: Malicious code in @c1-ease/bank (npm)
@c1-ease/bank = 3.0.0 → remove it | = 1.0.0 → remove it | = 0.0.1 → remove it | = 2.0.0 → remove it | = 2.0.1 → remove it | = 1.0.1 → remove it; +1 more
Why tagged?
- SCA from the title:
GHSA-q599-9j7q-8xf5: Maliciou
- SCA from the title:
GHSA-69rf-36f8-r3fm: Malicious code in autoloan (npm)
autoloan = 3.0.0 → remove it | = 0.0.1 → remove it | = 2.0.0 → remove it | = 1.1.0 → remove it
Why tagged?
- SCA from the title:
GHSA-69rf-36f8-r3fm: Maliciou
- SCA from the title:
GHSA-v352-9p9c-2wv7: Malicious code in @c1-ease/autoloan (npm)
@c1-ease/autoloan = 1.1.0 → remove it | = 1.0.1 → remove it | = 1.0.0 → remove it | = 3.0.0 → remove it | = 2.0.0 → remove it | = 2.0.1 → remove it; +1 more
Why tagged?
- SCA from the title:
GHSA-v352-9p9c-2wv7: Maliciou
- SCA from the title:
GHSA-j5h6-446w-9q9c: Malicious code in @c1-ease/card (npm)
@c1-ease/card = 0.0.1 → remove it | = 99.0.1 → remove it | = 1.0.1 → remove it | = 1.1.0 → remove it | = 1.0.0 → remove it | = 2.0.1 → remove it
Why tagged?
- SCA from the title:
GHSA-j5h6-446w-9q9c: Maliciou
- SCA from the title:
GHSA-4w4w-phqm-jfpm: Malicious code in @c1-ease/commerce (npm)
@c1-ease/commerce = 2.0.1 → remove it | = 2.0.0 → remove it | = 3.0.0 → remove it | = 1.1.0 → remove it | = 1.0.1 → remove it
Why tagged?
- SCA from the title:
GHSA-4w4w-phqm-jfpm: Maliciou
- SCA from the title:
GHSA-cxc9-87g6-qrj9: Malware in @wppconnect-team/wppconnect
@wppconnect-team/wppconnect = 2.4.1 → remove it
Why tagged?
- SCA from the title:
GHSA-cxc9-87g6-qrj9: Malware
- SCA from the title:
GHSA-w4wf-4398-p973: Malicious code in signed-manifest-guard (PyPI)
signed-manifest-guard = 0.1.7 → remove it
Why tagged?
- SCA from the title:
GHSA-w4wf-4398-p973: Maliciou
- SCA from the title:
GHSA-wqr9-48cj-55gj: Malicious code in instantscrape (PyPI)
instantscrape = 0.1.0 → remove it | = 0.1.5 → remove it | = 0.1.8 → remove it
Why tagged?
- SCA from the title:
GHSA-wqr9-48cj-55gj: Maliciou
- SCA from the title:
GnuPG Warns Critical GPGME Flaw Could Expose App Data via Malicious OpenPGP Keys
A malicious OpenPGP key with an unusually long user ID can trigger a critical memory bug in GPGME, the standard library that programs use to work with GnuPG. The GnuPG project warned yesterday that the flaw could be used to steal data from affected applications and has released…
Why tagged?
- Remediation from the excerpt:
ations and has released fixed versions. The bug, tracked as C
- Remediation from the excerpt:
GHSA-pgrg-83q3-w7vr: Malicious code in aia-b-locator-fe (npm)
aia-b-locator-fe = 1.0.3 → remove it
Why tagged?
- SCA from the title:
GHSA-pgrg-83q3-w7vr: Maliciou
- SCA from the title:
GHSA-r9wp-474x-c72c: Malware in @pkgship/frps-windows-amd64
@pkgship/frps-windows-amd64 = 0.71.1 → remove it
Why tagged?
- SCA from the title:
GHSA-r9wp-474x-c72c: Malware
- SCA from the title:
GHSA-23xm-8qc2-wp55: Malicious code in signed-manifest-updater (PyPI)
signed-manifest-updater = 0.1.5 → remove it
Why tagged?
- SCA from the title:
GHSA-23xm-8qc2-wp55: Maliciou
- SCA from the title:
GHSA-25qc-m4pw-2w8r / CVE-2026-122247: Budibase: Unauthenticated global-admin & database creation via tenant-confusion bypass of the one-time init guard (`POST /api/global/users/init`)
@budibase/server <= 3.38.1 → no fix
Why tagged?
- SCA from the title:
GHSA-25qc-m4pw-2w8r / CVE-202
- SCA from the title:
GHSA-r2q3-7m4h-63qg / CVE-2026-122244: Budibase: Cross-privilege Stored XSS in the Budibase Builder via broken HTML-escaping in `jsonFormatter.format()` rendered through `{@html}` in the CSP-less Builder origin
@budibase/server <= 3.38.1 → no fix
Why tagged?
- SCA from the title:
GHSA-r2q3-7m4h-63qg / CVE-202
- SCA from the title:
GHSA-53pm-wgxf-c6qf / CVE-2026-132276: wcmatch: Polynomial-time ReDoS when matching untrusted names against multi-star patterns (default flags)
wcmatch <= 11.1 → 11.2
Why tagged?
- SCA from the title:
GHSA-53pm-wgxf-c6qf / CVE-202
- SCA from the title:
GHSA-q87h-c5m7-659j / CVE-2026-132277: Inscriptis: Quadratic memory growth from sibling <table> elements in get_text()
inscriptis >= 2.0.0, <= 2.7.5 → 2.7.6
Why tagged?
- SCA from the title:
GHSA-q87h-c5m7-659j / CVE-202
- SCA from the title:
GHSA-555j-qj3j-c8jv / CVE-2026-132275: svglib: Exponential resource consumption via nested <use> references in svg2rlg
svglib <= 2.3.0 → 2.3.1
Why tagged?
- SCA from the title:
GHSA-555j-qj3j-c8jv / CVE-202
- SCA from the title:
GHSA-h57j-5f5m-789v / CVE-2026-104884: contao/core-bundle: Cross-site scripting in the frontend search results
contao/core-bundle >= 4.9.0, < 5.3.50 → 5.3.50 | >= 5.4.0-RC1, < 5.7.12 → 5.7.12
Why tagged?
- SCA from the title:
GHSA-h57j-5f5m-789v / CVE-202
- SCA from the title:
GHSA-r9qp-pqx5-8369 / CVE-2026-104883: contao/core-bundle: Non-admin users can self-grant permissions that implicitly make them administrators
contao/core-bundle >= 5.0.0, < 5.3.50 → 5.3.50 | >= 5.4.0-RC1, < 5.7.12 → 5.7.12
Why tagged?
- SCA from the title:
GHSA-r9qp-pqx5-8369 / CVE-202
- SCA from the title:
GHSA-23w9-4pg3-xwm3 / CVE-2026-104882: contao/core-bundle: Improper access control in the CSV import wizard
contao/core-bundle >= 5.0.0, < 5.3.50 → 5.3.50 | >= 5.4.0-RC1, < 5.7.12 → 5.7.12
Why tagged?
- SCA from the title:
GHSA-23w9-4pg3-xwm3 / CVE-202
- SCA from the title:
GHSA-3r9g-pfhv-3228 / CVE-2026-104881: contao/newsletter-bundle: Contao newsletter custom actions bypass channel-scoped authorization
contao/newsletter-bundle >= 5.0.0, < 5.3.50 → 5.3.50 | >= 5.4.0-RC1, < 5.7.12 → 5.7.12
Why tagged?
- SCA from the title:
GHSA-3r9g-pfhv-3228 / CVE-202
- SCA from the title:
GHSA-72jh-722p-rqr3 / CVE-2026-77331: memtomem-stm: Concurrent LTM recovery can duplicate reconnects or reuse a cancelled transport session
memtomem-stm >= 0.1.2, <= 0.1.33 → 0.1.34
Why tagged?
- SCA from the title:
GHSA-72jh-722p-rqr3 / CVE-202
- SCA from the title:
GHSA-43hx-xm7w-3mhj / CVE-2026-77332: memtomem-stm: Surfaced memory data can escape the Markdown compatibility boundary
memtomem-stm >= 0.1.0, <= 0.1.33 → 0.1.34
Why tagged?
- SCA from the title:
GHSA-43hx-xm7w-3mhj / CVE-202
- SCA from the title:
GHSA-jrjx-9jjw-747m / CVE-2026-77309: AIT-GUI route chain allows unauthenticated Python execution in server process
ait-gui >= 1.0.0, <= 2.5.0 → 2.5.1
Why tagged?
- SCA from the title:
GHSA-jrjx-9jjw-747m / CVE-202
- SCA from the title:
GHSA-qh76-45cr-8xrc / CVE-2026-61725: sevenz-rust2: decompress builds each output path as dest.join(entry.name()) with no traversal guard, allowing a crafted .7z to write files outside the destination (Zip-Slip)
sevenz-rust2 < 0.21.1 → 0.21.1
Why tagged?
- SCA from the title:
GHSA-qh76-45cr-8xrc / CVE-202
- SCA from the title:
GHSA-xxqp-5qx8-gj5q / CVE-2026-63341: Aedes has Uncaught Exception and Uncontrolled Resource Consumption
aedes < 1.1.1 → 1.1.1
Why tagged?
- SCA from the title:
GHSA-xxqp-5qx8-gj5q / CVE-202
- SCA from the title:
GHSA-p3j5-5hrq-p75h / CVE-2026-58254: nats-server Leaf node connections bypass Nats-Trace-Dest permission check
github.com/nats-io/nats-server/v2 < 2.12.8 → 2.12.8 | >= 2.14.0-RC.1, < 2.14.3 → 2.14.3
Why tagged?
- SCA from the title:
GHSA-p3j5-5hrq-p75h / CVE-202
- SCA from the title:
GHSA-rf8v-v97c-32r7: Malware in orion-overlord
orion-overlord >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-rf8v-v97c-32r7: Malware
- SCA from the title:
GHSA-jq64-f5cw-4m63: Malicious code in wouki-lipok (PyPI)
wouki-lipok = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-jq64-f5cw-4m63: Maliciou
- SCA from the title:
GHSA-4ccc-7rf5-f7fr: Malicious code in delta-nested-filter-tracer (PyPI)
delta-nested-filter-tracer = 1.0.0 → remove it | = 1.0.0.post1 → remove it
Why tagged?
- SCA from the title:
GHSA-4ccc-7rf5-f7fr: Maliciou
- SCA from the title:
GHSA-4qjx-cpx9-x936: Malicious code in pkgreg-buildprobe-16c409218045 (PyPI)
pkgreg-buildprobe-16c409218045 = 0.0.1 → remove it | = 0.0.2 → remove it
Why tagged?
- SCA from the title:
GHSA-4qjx-cpx9-x936: Maliciou
- SCA from the title:
GHSA-wgw6-fp43-67xp: Malicious code in identity-poc (npm)
identity-poc = 1.0.3 → remove it
Why tagged?
- SCA from the title:
GHSA-wgw6-fp43-67xp: Maliciou
- SCA from the title:
GHSA-j75q-4f87-cvr5: Malicious code in vreqtx-b5w3n-testmetest (npm)
vreqtx-b5w3n-testmetest = 1.0.1 → remove it
Why tagged?
- SCA from the title:
GHSA-j75q-4f87-cvr5: Maliciou
- SCA from the title:
GHSA-ggc8-jm8h-f86f: Malicious code in scope-token-fetch-vector (PyPI)
scope-token-fetch-vector = 1.0.0 → remove it | = 1.0.0.post1 → remove it
Why tagged?
- SCA from the title:
GHSA-ggc8-jm8h-f86f: Maliciou
- SCA from the title:
GHSA-8m2x-4x4x-cq8p: Malicious code in qzi2v-tttf1-testmetest (npm)
qzi2v-tttf1-testmetest = 1.0.1 → remove it
Why tagged?
- SCA from the title:
GHSA-8m2x-4x4x-cq8p: Maliciou
- SCA from the title:
GHSA-f4pg-5677-5vm5: Malicious code in xssdoctor-muse-task448-provider-runtime (npm)
xssdoctor-muse-task448-provider-runtime = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-f4pg-5677-5vm5: Maliciou
- SCA from the title:
GHSA-hgqv-p73h-wm6f: Malicious code in cijukop (PyPI)
cijukop = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-hgqv-p73h-wm6f: Maliciou
- SCA from the title:
GHSA-8hrc-gqpq-gwpv: Malicious code in testing1345py (PyPI)
testing1345py = 0.1.3 → remove it | = 0.1.4 → remove it
Why tagged?
- SCA from the title:
GHSA-8hrc-gqpq-gwpv: Maliciou
- SCA from the title:
GHSA-4xj4-jwq4-jqwf: Malicious code in @kropa/baileys (npm)
@kropa/baileys = 1.0.0 → remove it | = 1.0.3 → remove it | = 1.0.2 → remove it | = 1.0.1 → remove it
Why tagged?
- SCA from the title:
GHSA-4xj4-jwq4-jqwf: Maliciou
- SCA from the title:
GHSA-g4vg-qmwm-vh4c: Malicious code in @kropaku/baileys (npm)
@kropaku/baileys = 6.7.23 → remove it | = 6.7.22 → remove it | = 6.7.21 → remove it | = 6.7.24 → remove it | = 6.7.20 → remove it
Why tagged?
- SCA from the title:
GHSA-g4vg-qmwm-vh4c: Maliciou
- SCA from the title:
GHSA-v33p-qh9f-g4rp: Malicious code in @expo-probe-ff8e2b/snack-probe-c2a16 (npm)
@expo-probe-ff8e2b/snack-probe-c2a16 = 1.0.0 → remove it | = 1.0.1 → remove it
Why tagged?
- SCA from the title:
GHSA-v33p-qh9f-g4rp: Maliciou
- SCA from the title:
GHSA-9v66-fc47-m28q: Malware in swaplearn-cli
swaplearn-cli >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-9v66-fc47-m28q: Malware
- SCA from the title:
GHSA-2xxf-xq83-2h3q: Malware in @sapp1/baileys-pro
@sapp1/baileys-pro = 1.0.1 → remove it
Why tagged?
- SCA from the title:
GHSA-2xxf-xq83-2h3q: Malware
- SCA from the title:
GHSA-7r7x-px4j-w4jg: Malware in dsh-blue-team-mode
dsh-blue-team-mode = 3.0.0-beta.18 → remove it | = 3.0.0-beta.17 → remove it | = 3.0.0-beta.20 → remove it
Why tagged?
- SCA from the title:
GHSA-7r7x-px4j-w4jg: Malware
- SCA from the title:
GHSA-v223-q8vf-c837: Malware in alwaysaqioo
alwaysaqioo = 1.1.1 → remove it | = 1.1.2 → remove it | = 1.1.3 → remove it | = 1.1.5 → remove it
Why tagged?
- SCA from the title:
GHSA-v223-q8vf-c837: Malware
- SCA from the title:
GHSA-24gg-4qq2-6r2g: Malware in tonty-tech-interviews
tonty-tech-interviews >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-24gg-4qq2-6r2g: Malware
- SCA from the title:
GHSA-wqcq-qg5g-jm7r: Malware in @zetagoaurum-socket/wasocket
@zetagoaurum-socket/wasocket = 2.1.0 → remove it | = 2.1.1 → remove it | = 2.1.2 → remove it | = 2.1.3 → remove it | = 2.1.4 → remove it | = 2.1.5 → remove it; +10 more
Why tagged?
- SCA from the title:
GHSA-wqcq-qg5g-jm7r: Malware
- SCA from the title:
GHSA-gjrr-f7w5-4j4g: Malware in @violetix/baileys
@violetix/baileys = 0.0.0-stage → remove it | = 0.3.18 → remove it | = 0.4.0 → remove it | = 0.5.0 → remove it | = 0.5.1 → remove it | = 0.5.2 → remove it; +7 more
Why tagged?
- SCA from the title:
GHSA-gjrr-f7w5-4j4g: Malware
- SCA from the title:
How Cloudflare WAF helps protect against phpAfterShell and other critical PHP flaws
phpAfterShell is a critical flaw in PHP's default session handler that can lead to code execution. Cloudflare WAF blocks it for all customers, including Free plans, and adds new rules for other PHP flaws fixed in the same release.
Why tagged?
- Remediation from the excerpt:
les for other PHP flaws fixed in the same release.
- Remediation from the excerpt:
GHSA-94wh-c496-hm43: Malware in @basis-theory-elements/api-client
@basis-theory-elements/api-client >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-94wh-c496-hm43: Malware
- SCA from the title:
GHSA-5g25-2vc4-7gfh: Malware in @vanzky/baileys
@vanzky/baileys >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-5g25-2vc4-7gfh: Malware
- SCA from the title:
GHSA-646c-v3qw-f7f9: Malware in @trashcore/baileys
@trashcore/baileys = 4.0.0 → remove it | = 4.0.1 → remove it | = 4.0.2 → remove it | = 4.0.5 → remove it | = 4.0.6 → remove it | = 4.0.7 → remove it; +20 more
Why tagged?
- SCA from the title:
GHSA-646c-v3qw-f7f9: Malware
- SCA from the title:
GHSA-w5w9-7whq-mg6h: Malware in @zanxiky/baileys
@zanxiky/baileys >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-w5w9-7whq-mg6h: Malware
- SCA from the title:
GHSA-6fm5-pgx8-4crc: Malware in @yshtxxproject/baileys
@yshtxxproject/baileys >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-6fm5-pgx8-4crc: Malware
- SCA from the title:
GHSA-w29j-8x2j-rrj6: Malware in @postman-cse/okta-aio-darwin-arm64
@postman-cse/okta-aio-darwin-arm64 = 0.8.10 → remove it | = 0.8.11 → remove it | = 0.9.0 → remove it | = 0.9.1 → remove it | = 0.10.0 → remove it | = 0.10.1 → remove it; +15 more
Why tagged?
- SCA from the title:
GHSA-w29j-8x2j-rrj6: Malware
- SCA from the title:
GHSA-f329-9g9w-rc6v: Malware in lyxe-baileys
lyxe-baileys >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-f329-9g9w-rc6v: Malware
- SCA from the title:
GHSA-79f8-6qm5-fr58: Malware in @thepayulink/server
@thepayulink/server = 2.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-79f8-6qm5-fr58: Malware
- SCA from the title:
GHSA-9qcw-jqhm-rpg5: Malware in arshadahmed
arshadahmed = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-9qcw-jqhm-rpg5: Malware
- SCA from the title:
GHSA-3xvc-c2xw-876g: Malware in arifali
arifali = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-3xvc-c2xw-876g: Malware
- SCA from the title:
GHSA-m249-7c47-vgj8: Malware in apasih-me-polda
apasih-me-polda = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-m249-7c47-vgj8: Malware
- SCA from the title:
GHSA-qqvg-29x3-2xxq: Malware in apasih-ledong-po
apasih-ledong-po = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-qqvg-29x3-2xxq: Malware
- SCA from the title:
GHSA-3v73-9mj7-hjr2: Malware in apasih-ledan-puakfi
apasih-ledan-puakfi = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-3v73-9mj7-hjr2: Malware
- SCA from the title:
WhatsApp Patches 3 Security Flaws, Including Android Bug Suspected of Use in Scams
Meta-owned WhatsApp has addressed security vulnerabilities, including one impacting its Android app that it suspects may have been exploited in connection with scam messages. The vulnerability, tracked as CVE-2026-23871, has been described as a case of incomplete validation of…
Why tagged?
- Remediation from the title:
WhatsApp Patches 3 Security Flaws, Inclu
- Remediation from the title:
GHSA-9hx5-mqf4-wh7r: Malware in apasih-leda-pk
apasih-leda-pk = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-9hx5-mqf4-wh7r: Malware
- SCA from the title:
GHSA-w76f-qf34-79mp: Malware in apasih-led-pokiari
apasih-led-pokiari = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-w76f-qf34-79mp: Malware
- SCA from the title:
GHSA-cprp-4fgg-48m6: Malware in apakri
apakri = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-cprp-4fgg-48m6: Malware
- SCA from the title:
GHSA-f977-cj53-f9g2: Malware in antoniosouza
antoniosouza = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-f977-cj53-f9g2: Malware
- SCA from the title:
GHSA-83q9-4x8m-hmjj: Malware in anita-buy-mag
anita-buy-mag = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-83q9-4x8m-hmjj: Malware
- SCA from the title:
GHSA-w2jc-956j-48qw: Malware in anisyafira
anisyafira = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-w2jc-956j-48qw: Malware
- SCA from the title:
GHSA-fq86-p97c-8r66: Malware in animab
animab = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-fq86-p97c-8r66: Malware
- SCA from the title:
GHSA-mhwh-34xx-46j9: Malware in anidata-hopanud-mai
anidata-hopanud-mai = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-mhwh-34xx-46j9: Malware
- SCA from the title:
GHSA-4mq9-pj85-7r39: Malware in anidata-hd-madidsa
anidata-hd-madidsa = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-4mq9-pj85-7r39: Malware
- SCA from the title:
GHSA-mwj2-r2v8-vj88: Malware in anidata-haulid-mubda
anidata-haulid-mubda = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-mwj2-r2v8-vj88: Malware
- SCA from the title:
GHSA-cf7f-vc3h-26qp: Malware in ameliarichards
ameliarichards = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-cf7f-vc3h-26qp: Malware
- SCA from the title:
GHSA-3mc8-4chr-cc2r: Malware in ameliagordonlucaswalsh
ameliagordonlucaswalsh = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-3mc8-4chr-cc2r: Malware
- SCA from the title:
GHSA-gx8q-jq3c-79fr: Malware in ameerjamal
ameerjamal = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-gx8q-jq3c-79fr: Malware
- SCA from the title:
GHSA-fx2p-5qq8-2q73: Malware in alaaddindar
alaaddindar = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-fx2p-5qq8-2q73: Malware
- SCA from the title:
GHSA-x276-5hw5-w9q7: Malware in akifsaeed
akifsaeed = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-x276-5hw5-w9q7: Malware
- SCA from the title:
GHSA-f7pc-6mj6-3fvh: Malware in akanabi-alaigah-aimuava
akanabi-alaigah-aimuava = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-f7pc-6mj6-3fvh: Malware
- SCA from the title:
GHSA-9j29-6pq4-4x7g: Malware in akanabi-abia-baigbub
akanabi-abia-baigbub = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-9j29-6pq4-4x7g: Malware
- SCA from the title:
GHSA-cg75-5x4j-6x3m: Malware in akanabi-abia-babu
akanabi-abia-babu = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-cg75-5x4j-6x3m: Malware
- SCA from the title:
GHSA-8c8r-7wm8-rcwm: Malware in akabia-aligufi-av
akabia-aligufi-av = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-8c8r-7wm8-rcwm: Malware
- SCA from the title:
GHSA-495g-7fqv-pm25: Malware in ajmalzaki
ajmalzaki = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-495g-7fqv-pm25: Malware
- SCA from the title:
GHSA-h424-4vc8-w6f5: Malware in aiyuyia-iaydut-daina
aiyuyia-iaydut-daina = 1.1.2 → remove it
Why tagged?
- SCA from the title:
GHSA-h424-4vc8-w6f5: Malware
- SCA from the title:
GHSA-6q4g-3vrj-w5c6: Malware in aiboa-molipe-aramiia
aiboa-molipe-aramiia = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-6q4g-3vrj-w5c6: Malware
- SCA from the title:
GHSA-m5vg-59x6-6p6p: Malware in aiboa-milipe-apmuma
aiboa-milipe-apmuma = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-m5vg-59x6-6p6p: Malware
- SCA from the title:
GHSA-c8x2-qg96-2h24: Malware in anastasia-soluble-pot
anastasia-soluble-pot = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-c8x2-qg96-2h24: Malware
- SCA from the title:
GHSA-mw52-h95g-c4q2: Malware in analusia-aki-iniu
analusia-aki-iniu = 1.3.3 → remove it
Why tagged?
- SCA from the title:
GHSA-mw52-h95g-c4q2: Malware
- SCA from the title:
GHSA-rwc7-j78x-qwgw: Malware in anala-akin-inuuli
anala-akin-inuuli = 1.3.3 → remove it
Why tagged?
- SCA from the title:
GHSA-rwc7-j78x-qwgw: Malware
- SCA from the title:
GHSA-58cx-x5p7-642p: Malware in anala-akiman-inuli
anala-akiman-inuli = 1.3.3 → remove it
Why tagged?
- SCA from the title:
GHSA-58cx-x5p7-642p: Malware
- SCA from the title:
GHSA-9435-p5jr-pvgh: Malware in anaisi-pafnolai-asigoga
anaisi-pafnolai-asigoga = 1.3.3 → remove it
Why tagged?
- SCA from the title:
GHSA-9435-p5jr-pvgh: Malware
- SCA from the title:
GHSA-qj3g-mgf4-5mfx: Malware in anais-papoa-0pipaia
anais-papoa-0pipaia = 1.3.3 → remove it
Why tagged?
- SCA from the title:
GHSA-qj3g-mgf4-5mfx: Malware
- SCA from the title:
GHSA-mvw4-7rfg-8c99: Malware in anabuyil-na0n-lukiahuas
anabuyil-na0n-lukiahuas = 1.3.3 → remove it
Why tagged?
- SCA from the title:
GHSA-mvw4-7rfg-8c99: Malware
- SCA from the title:
GHSA-mvxr-rjfh-jxx6: Malware in anabuyil-na0n-luiahuas
anabuyil-na0n-luiahuas = 1.3.3 → remove it
Why tagged?
- SCA from the title:
GHSA-mvxr-rjfh-jxx6: Malware
- SCA from the title:
GHSA-rg3w-v6c5-rp36: Malware in anabuyil-inupava-ninni
anabuyil-inupava-ninni = 1.3.3 → remove it
Why tagged?
- SCA from the title:
GHSA-rg3w-v6c5-rp36: Malware
- SCA from the title:
GHSA-948f-976v-f4gw: Malware in anabuyil-inpa-ninni
anabuyil-inpa-ninni = 1.3.3 → remove it
Why tagged?
- SCA from the title:
GHSA-948f-976v-f4gw: Malware
- SCA from the title:
GHSA-g3p9-hpj2-g74p: Malware in anabuyil-inanhu-ninni
anabuyil-inanhu-ninni = 1.3.3 → remove it
Why tagged?
- SCA from the title:
GHSA-g3p9-hpj2-g74p: Malware
- SCA from the title:
GHSA-w4qw-m8x9-g8w5: Malware in anabuyi-inuba-ninni
anabuyi-inuba-ninni = 1.3.3 → remove it
Why tagged?
- SCA from the title:
GHSA-w4qw-m8x9-g8w5: Malware
- SCA from the title:
GHSA-q6q4-4c8q-c88j: Malware in anabuyi-inu-ninni
anabuyi-inu-ninni = 1.3.3 → remove it
Why tagged?
- SCA from the title:
GHSA-q6q4-4c8q-c88j: Malware
- SCA from the title:
GHSA-rxwc-4r9f-4jgv: Malware in amjadtaheem
amjadtaheem = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-rxwc-4r9f-4jgv: Malware
- SCA from the title:
GHSA-pfj7-pg2r-xpj8: Malware in amjadatef
amjadatef = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-pfj7-pg2r-xpj8: Malware
- SCA from the title:
GHSA-2r97-8h35-x4j8: Malware in aminchocolat
aminchocolat = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-2r97-8h35-x4j8: Malware
- SCA from the title:
GHSA-385h-j8j7-fx22: Malware in aciyuyia-iadut-daina
aciyuyia-iadut-daina = 1.1.2 → remove it
Why tagged?
- SCA from the title:
GHSA-385h-j8j7-fx22: Malware
- SCA from the title:
GHSA-v3cr-c366-8p7j: Malware in aciyudua-iadut-daina
aciyudua-iadut-daina = 1.1.2 → remove it
Why tagged?
- SCA from the title:
GHSA-v3cr-c366-8p7j: Malware
- SCA from the title:
GHSA-77f2-4wmf-rwgg: Malware in aciyua-iduat-doauuufa
aciyua-iduat-doauuufa = 1.1.2 → remove it
Why tagged?
- SCA from the title:
GHSA-77f2-4wmf-rwgg: Malware
- SCA from the title:
GHSA-9rv8-9hvg-92mq / CVE-2026-35376: chcon: recursive relabel not anchored to traversal dirfd (TOCTOU)
uu_chcon <= 0.9.0 → 0.10.0
Why tagged?
- SCA from the title:
GHSA-9rv8-9hvg-92mq / CVE-202
- SCA from the title:
GHSA-xhrc-7f76-vh96 / CVE-2026-35377: uu_env incorrectly rejects backslashes within single-quoted strings accepted by GNU env
uu_env <= 0.9.0 → 0.10.0
Why tagged?
- SCA from the title:
GHSA-xhrc-7f76-vh96 / CVE-202
- SCA from the title:
GHSA-fjjq-8hw5-cf9f / CVE-2026-35374: split: TOCTOU output-open allows truncating a swapped file
uu_split <= 0.9.0 → 0.10.0
Why tagged?
- SCA from the title:
GHSA-fjjq-8hw5-cf9f / CVE-202
- SCA from the title:
GHSA-6499-jgj4-2wpf / CVE-2026-104773: CKAN: Session Fixation in Registration View
ckan < 2.10.11 → 2.10.11 | >= 2.11.0, < 2.11.6 → 2.11.6
Why tagged?
- SCA from the title:
GHSA-6499-jgj4-2wpf / CVE-202
- SCA from the title:
GHSA-cg26-4c6j-2x8h / CVE-2026-69133: netty-incubator-codec-ohttp: OHTTP codecs retain consumed outer cumulation buffers after completed exchanges
io.netty.incubator:netty-incubator-codec-ohttp >= 0.0.20.Final, <= 0.0.26.Final → 0.0.27.Final
Why tagged?
- SCA from the title:
GHSA-cg26-4c6j-2x8h / CVE-202
- SCA from the title:
WhatsApp Fixes Flaw Uncovered While Disrupting Scam Campaign
Tracked as CVE-2026-23871, the vulnerability was found by WhatsApp’s security team, and it may have been used to make scam messages more credible.
Why tagged?
- Remediation from the title:
WhatsApp Fixes Flaw Uncovered While Disrupt
- Remediation from the title:
GHSA-x72p-hmqp-46hw / CVE-2026-105803: Git LFS may execute arbitrary commands via crafted Git LFS configurations
github.com/git-lfs/git-lfs >= 1.3.0, <= 2.13.3 → no fix; github.com/git-lfs/git-lfs/v3 >= 3.0.0, < 3.8.1 → 3.8.1 · partly fixed
Why tagged?
- SCA from the title:
GHSA-x72p-hmqp-46hw / CVE-202
- SCA from the title:
GHSA-xrgv-7vx6-5vx6 / CVE-2026-105802: Git LFS may execute arbitrary commands via crafted Git configurations
github.com/git-lfs/git-lfs >= 0.6.0, <= 2.13.3 → no fix; github.com/git-lfs/git-lfs/v3 >= 3.0.0, < 3.8.1 → 3.8.1 · partly fixed
Why tagged?
- SCA from the title:
GHSA-xrgv-7vx6-5vx6 / CVE-202
- SCA from the title:
GHSA-3h6w-xcw3-9xjj / CVE-2026-104885: OpenRemote: Cross-realm MQTT session disconnect without authorization
io.openremote:openremote-manager < 1.31.0 → 1.31.0
Why tagged?
- SCA from the title:
GHSA-3h6w-xcw3-9xjj / CVE-202
- SCA from the title:
GHSA-prhx-9q2h-ph2x / CVE-2026-103026: Paymenter: Unauthenticated arbitrary method invocation in Livewire components
paymenter/paymenter <= 1.5.6 → 1.5.7
Why tagged?
- SCA from the title:
GHSA-prhx-9q2h-ph2x / CVE-202
- SCA from the title:
GHSA-vcx7-pfrh-mcfg / CVE-2026-115565: storyblok-backup: Stored path traversal via unsanitized Storyblok component names in backup output
storyblok-backup <= 0.7.0 → 0.7.1
Why tagged?
- SCA from the title:
GHSA-vcx7-pfrh-mcfg / CVE-202
- SCA from the title:
GHSA-wcqj-wx85-c75p / CVE-2026-130176: aMQTT: Denial of Service (DoS) via Memory Leak in Unmanaged QoS 2 Session Handshakes
amqtt >= 0.11.0, <= 0.12.0 → 0.12.1
Why tagged?
- SCA from the title:
GHSA-wcqj-wx85-c75p / CVE-202
- SCA from the title:
GHSA-9657-8vc2-7g2p / CVE-2026-115463: Poweradmin: The email second factor is an mt_rand() six-digit code verified with no attempt limit or lockout, so an attacker holding the password can brute-force it within the validity window
poweradmin/poweradmin >= 4.0.0, < 4.2.6 → 4.2.6 | >= 4.3.0, < 4.3.5 → 4.3.5 | >= 4.4.0, < 4.4.1 → 4.4.1
Why tagged?
- SCA from the title:
GHSA-9657-8vc2-7g2p / CVE-202
- SCA from the title:
GHSA-4hrh-34w3-5ww8 / CVE-2026-104099: Fabio: Access-control bypass through unnormalized request paths
github.com/fabiolb/fabio < 1.7.3 → 1.7.3
Why tagged?
- SCA from the title:
GHSA-4hrh-34w3-5ww8 / CVE-202
- SCA from the title:
GHSA-x7xj-4j4f-88xr / CVE-2026-69261: Git LFS may leak HTTP headers after redirections
github.com/git-lfs/git-lfs >= 0.5.0, <= 2.13.3 → no fix; github.com/git-lfs/git-lfs/v3 >= 3.0.0, < 3.8.1 → 3.8.1 · partly fixed
Why tagged?
- SCA from the title:
GHSA-x7xj-4j4f-88xr / CVE-202
- SCA from the title:
GHSA-w3f2-pr6x-wwjc / CVE-2026-69260: Git LFS may attempt arbitrary remote commands via crafted SSH URLs
github.com/git-lfs/git-lfs >= 0.5.0, <= 2.13.3 → no fix; github.com/git-lfs/git-lfs/v3 >= 3.0.0, < 3.8.1 → 3.8.1 · partly fixed
Why tagged?
- SCA from the title:
GHSA-w3f2-pr6x-wwjc / CVE-202
- SCA from the title:
GHSA-66q9-mxf2-xqw6 / CVE-2026-103035: TeamPass folder re-parenting authorization bypass
nilsteampassnet/TeamPass < 3.2.2.0 → 3.2.2.0
Why tagged?
- SCA from the title:
GHSA-66q9-mxf2-xqw6 / CVE-202
- SCA from the title:
GHSA-2hjf-7455-w946 / CVE-2026-104199: aMQTT: Inefficient Regular Expression Complexity and Uncontrolled Resource Consumption and Improper Input Validation
amqtt >= 0.11.0, <= 0.11.3 → 0.11.4
Why tagged?
- SCA from the title:
GHSA-2hjf-7455-w946 / CVE-202
- SCA from the title:
GHSA-hghq-53p7-c582 / CVE-2026-115578: go-guerrilla crashes on a bare XCLIENT command (7-byte slice off-by-one panic)
github.com/phires/go-guerrilla = 1.6.7 → no fix | < 1.6.7-1 → 1.6.7-1 · partly fixed
Why tagged?
- SCA from the title:
GHSA-hghq-53p7-c582 / CVE-202
- SCA from the title:
GHSA-v9v2-98xq-627c / CVE-2026-104129: pREST _groupby function-expression SQL injection (incomplete fix of CVE-2025-58450)
github.com/prest/prest <= 1.5.5 → no fix; github.com/prest/prest/v2 <= 2.3.0 → 2.4.0 · partly fixed
Why tagged?
- SCA from the title:
GHSA-v9v2-98xq-627c / CVE-202
- SCA from the title:
GHSA-3g82-77xr-68x5 / CVE-2026-63386: js-toml allows uncontrolled recursion in `load()` leading `RangeError` (stack exhaustion) on deeply nested input
js-toml < 1.1.3 → 1.1.3
Why tagged?
- SCA from the title:
GHSA-3g82-77xr-68x5 / CVE-202
- SCA from the title:
GHSA-x6w4-f264-3vvr / CVE-2026-63184: Refitter: Unrestricted OpenAPI references permit build-host SSRF and file inclusion
Refitter < 2.1.1 → 2.1.1
Why tagged?
- SCA from the title:
GHSA-x6w4-f264-3vvr / CVE-202
- SCA from the title:
GHSA-jwgx-mp9m-jwcr / CVE-2026-58192: appium allows unauthenticated arbitrary file/directory deletion in @appium/storage-plugin
@appium/storage-plugin < 1.1.6 → 1.1.6
Why tagged?
- SCA from the title:
GHSA-jwgx-mp9m-jwcr / CVE-202
- SCA from the title:
GHSA-jcx6-j558-wppc: Malware in @metagl/sdk-render
@metagl/sdk-render = 4.0.6 → remove it
Why tagged?
- SCA from the title:
GHSA-jcx6-j558-wppc: Malware
- SCA from the title:
GHSA-xgr8-c5gp-x7xf: Malware in @corepassinc/remy-core-bin-win32-x64
@corepassinc/remy-core-bin-win32-x64 = 0.1.0-rc.30 → remove it
Why tagged?
- SCA from the title:
GHSA-xgr8-c5gp-x7xf: Malware
- SCA from the title:
GHSA-h82f-cjm4-g22r: Malware in @guicai777/mcp-doctor
@guicai777/mcp-doctor >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-h82f-cjm4-g22r: Malware
- AI Security from the title:
GHSA-h82f-cjm4-g22r: Malware in @guicai777/mcp-doctor
- SCA from the title:
GHSA-6r85-j4v5-27rf: Malware in mock-data-sdk
mock-data-sdk >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-6r85-j4v5-27rf: Malware
- SCA from the title:
GHSA-8j58-xfpr-cqfv: Malware in motionframe-plugins
motionframe-plugins >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-8j58-xfpr-cqfv: Malware
- SCA from the title:
GHSA-v2fg-x378-42g4: Malware in @motionlib/framer-motion
@motionlib/framer-motion >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-v2fg-x378-42g4: Malware
- SCA from the title:
Linux KVM Flaw CVE-2026-99312 Lets Guest VMs Access Host Memory on AMD Hosts
A flaw in KVM, the hypervisor built into the Linux kernel, let researchers read about 127 GB of a cloud server's memory from inside a virtual machine of their own on DigitalOcean. On a shared server, that memory can include other customers' virtual machines. The flaw, tracked…
F5 releases emergency patches for critical BIG-IP RCE flaws
US cybersecurity company F5 warned customers to patch five critical BIG-IP vulnerabilities that attackers can exploit to trigger denial-of-service (DoS) or gain remote code execution. [...]
Why tagged?
- Remediation from the title:
F5 releases emergency patches for critical BIG-IP RCE
- Remediation from the title:
SonicWall Warns Gen 6 Firewalls Won't Get Security Patches, Even for Critical Flaws
SonicWall has urged all customers still running Generation 6 firewalls to retire and replace them immediately and stop exposing the devices on the internet edge, citing security risks fueled by AI-assisted attacks. "Attackers now use automation and AI to find and exploit…
Why tagged?
- Remediation from the title:
alls Won't Get Security Patches, Even for Critical Flaw
- Remediation from the title:
GHSA-gmwr-j73c-6xw3: Malware in mayx-blog
mayx-blog = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-gmwr-j73c-6xw3: Malware
- SCA from the title:
GHSA-vwr8-p7j8-qqxg: Malicious code in @fedfub/string-utils (npm)
@fedfub/string-utils = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-vwr8-p7j8-qqxg: Maliciou
- SCA from the title:
GHSA-q6xv-rqvq-8h46: Malicious code in vcdxg-eavtg-util (npm)
vcdxg-eavtg-util = 1.0.1 → remove it
Why tagged?
- SCA from the title:
GHSA-q6xv-rqvq-8h46: Maliciou
- SCA from the title:
GHSA-642c-p559-rmr5: Malicious code in truffle-kit (npm)
truffle-kit = 3.3.2 → remove it
Why tagged?
- SCA from the title:
GHSA-642c-p559-rmr5: Maliciou
- SCA from the title:
GHSA-f76h-3xwf-v78w: Malicious code in @ikyerza/baileys (npm)
@ikyerza/baileys = 1.0.0 → remove it | = 1.1.1 → remove it | = 1.2.0 → remove it
Why tagged?
- SCA from the title:
GHSA-f76h-3xwf-v78w: Maliciou
- SCA from the title:
GHSA-4rf3-5pmj-pw8m: Malicious code in @ikyzanx/baileys (npm)
@ikyzanx/baileys = 8.5.6 → remove it
Why tagged?
- SCA from the title:
GHSA-4rf3-5pmj-pw8m: Maliciou
- SCA from the title:
GHSA-h5f6-w383-w67g: Malicious code in @izi-coder/baileys (npm)
@izi-coder/baileys = 2.0.5 → remove it | = 6.0.9 → remove it | = 6.0.10 → remove it
Why tagged?
- SCA from the title:
GHSA-h5f6-w383-w67g: Maliciou
- SCA from the title:
GHSA-m77j-jgx5-q3j7: Malicious code in @fedfub/utils (npm)
@fedfub/utils = 1.0.1 → remove it
Why tagged?
- SCA from the title:
GHSA-m77j-jgx5-q3j7: Maliciou
- SCA from the title:
GHSA-7ppq-5qfr-6796: Malicious code in vite-plugin-bar-plus (npm)
vite-plugin-bar-plus = 1.0.47 → remove it
Why tagged?
- SCA from the title:
GHSA-7ppq-5qfr-6796: Maliciou
- SCA from the title:
GHSA-mq6r-xww7-j53j: Malicious code in @iky-erza/baileys (npm)
@iky-erza/baileys = 0.1.0 → remove it
Why tagged?
- SCA from the title:
GHSA-mq6r-xww7-j53j: Maliciou
- SCA from the title:
GHSA-jrfq-g54q-gmc8: Malicious code in scanstudy-pointer-bat (npm)
scanstudy-pointer-bat = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-jrfq-g54q-gmc8: Maliciou
- SCA from the title:
GHSA-j9r4-5g27-w8rx: Malicious code in @kingorwot/my-baileys (npm)
@kingorwot/my-baileys = 2.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-j9r4-5g27-w8rx: Maliciou
- SCA from the title:
GHSA-vxx3-mjmc-wgj8: Malicious code in @guicai777/mcp-doctor (npm)
@guicai777/mcp-doctor = 1.0.1 → remove it
Why tagged?
- SCA from the title:
GHSA-vxx3-mjmc-wgj8: Maliciou
- AI Security from the title:
GHSA-vxx3-mjmc-wgj8: Malicious code in @guicai777/mcp-doctor (npm)
- SCA from the title:
GHSA-qhrc-mfjw-xwq3: Malicious code in @eryxenx/fca (npm)
@eryxenx/fca = 1.3.2 → remove it | = 1.3.1 → remove it | = 1.3.0 → remove it
Why tagged?
- SCA from the title:
GHSA-qhrc-mfjw-xwq3: Maliciou
- SCA from the title:
GHSA-m6vr-gmw5-vfv7: Malicious code in retry-utils-testmetest (npm)
retry-utils-testmetest = 1.0.3 → remove it
Why tagged?
- SCA from the title:
GHSA-m6vr-gmw5-vfv7: Maliciou
- SCA from the title:
GHSA-cq9c-m7g7-f925: Malicious code in promise-retry-utils-testmetest (npm)
promise-retry-utils-testmetest = 1.0.1 → remove it
Why tagged?
- SCA from the title:
GHSA-cq9c-m7g7-f925: Maliciou
- SCA from the title:
GHSA-5q5c-h8xj-h3fp: Malicious code in mrcl2suhail (PyPI)
MRCL2Suhail = 1.0.1 → remove it | = 1.0.3 → remove it | = 1.0.4 → remove it | = 1.0.2 → remove it | = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-5q5c-h8xj-h3fp: Maliciou
- SCA from the title:
GHSA-f3g9-pmww-pww3: Malicious code in mrcl2 (PyPI)
MRCL2 = 1.0.5 → remove it | = 1.0.2 → remove it | = 1.0.1 → remove it | = 1.0.3 → remove it | = 1.0.4 → remove it
Why tagged?
- SCA from the title:
GHSA-f3g9-pmww-pww3: Maliciou
- SCA from the title:
GHSA-r4j6-q34r-gc6j: Malicious code in stream-buffer-utils-testmetest (npm)
stream-buffer-utils-testmetest = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-r4j6-q34r-gc6j: Maliciou
- SCA from the title:
GHSA-33v7-c769-3ww7: Malicious code in @awazevr/mfe-common.contexts.guest-auth (npm)
@awazevr/mfe-common.contexts.guest-auth = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-33v7-c769-3ww7: Maliciou
- SCA from the title:
GHSA-w7vf-pf93-jgpv: Malicious code in spencer-braincore (npm)
spencer-braincore = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-w7vf-pf93-jgpv: Maliciou
- SCA from the title:
GHSA-8rw9-x9m5-7353: Malware in @zaiinlin/bails
@zaiinlin/bails >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-8rw9-x9m5-7353: Malware
- SCA from the title:
GHSA-phch-78ch-wpcc: Malware in smfos-bskdz-util
smfos-bskdz-util >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-phch-78ch-wpcc: Malware
- SCA from the title:
GHSA-h68g-7c77-4w37: Malware in nuadg-jhtvh-util
nuadg-jhtvh-util >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-h68g-7c77-4w37: Malware
- SCA from the title:
GHSA-6wmj-hgpg-2pp6: Malware in vcnwi-ihpgp-util
vcnwi-ihpgp-util >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-6wmj-hgpg-2pp6: Malware
- SCA from the title:
GHSA-hq35-gwxr-qq5x: Malware in tsbwt-hawsi-util
tsbwt-hawsi-util >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-hq35-gwxr-qq5x: Malware
- SCA from the title:
GHSA-vm96-5m7m-hr25: Malware in jmrwd-gjdob-util
jmrwd-gjdob-util >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-vm96-5m7m-hr25: Malware
- SCA from the title:
GHSA-6gpf-476p-c87j: Malware in fcefi-wdojs-util
fcefi-wdojs-util >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-6gpf-476p-c87j: Malware
- SCA from the title:
GHSA-6p2g-3r68-5j5w: Malware in glbkm-vrnpk-util
glbkm-vrnpk-util >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-6p2g-3r68-5j5w: Malware
- SCA from the title:
GHSA-6wpr-mmgq-xj72: Malware in csvmw-glair-util
csvmw-glair-util >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-6wpr-mmgq-xj72: Malware
- SCA from the title:
GHSA-r3pq-mfc8-4c4f: Malware in piepa-yfcbf-util
piepa-yfcbf-util >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-r3pq-mfc8-4c4f: Malware
- SCA from the title:
GHSA-p65r-r93m-c4mj: Malware in oubkt-krxpo-util
oubkt-krxpo-util >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-p65r-r93m-c4mj: Malware
- SCA from the title:
GHSA-5x2f-rv2j-gxvc: Malware in qtfdd-lnrwx-util
qtfdd-lnrwx-util >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-5x2f-rv2j-gxvc: Malware
- SCA from the title:
GHSA-c2cw-ccqv-pghc: Malware in nhhhh-yhejl-util
nhhhh-yhejl-util >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-c2cw-ccqv-pghc: Malware
- SCA from the title:
GHSA-frxp-365q-8p36: Malware in teahy-znrpz-util
teahy-znrpz-util >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-frxp-365q-8p36: Malware
- SCA from the title:
GHSA-gcx6-6r3h-7cvr: Malware in vojmd-ajgkr-util
vojmd-ajgkr-util >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-gcx6-6r3h-7cvr: Malware
- SCA from the title:
GHSA-4ffv-gw64-v99f: Malware in xueoj-vjtof-util
xueoj-vjtof-util >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-4ffv-gw64-v99f: Malware
- SCA from the title:
GHSA-c5fp-459q-c9pp: Malware in dxrs-dos
dxrs-dos >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-c5fp-459q-c9pp: Malware
- SCA from the title:
GHSA-v97v-7r82-xcjg: Malicious code in certify-web (PyPI)
certify-web = 0.1.3 → remove it
Why tagged?
- SCA from the title:
GHSA-v97v-7r82-xcjg: Maliciou
- SCA from the title:
GHSA-ghgg-v8r8-pfc3: Malicious code in sirens-lamentt (npm)
sirens-lamentt = 99.0.2 → remove it
Why tagged?
- SCA from the title:
GHSA-ghgg-v8r8-pfc3: Maliciou
- SCA from the title:
GHSA-822g-7r9h-j5w4: Malicious code in webhook-easy (npm)
webhook-easy = 1.1.0 → remove it
Why tagged?
- SCA from the title:
GHSA-822g-7r9h-j5w4: Maliciou
- SCA from the title:
GHSA-fg8p-3m89-pwhf: Malicious code in @cexy/wonfca (npm)
@cexy/wonfca = 1.2.2 → remove it | = 1.2.1 → remove it
Why tagged?
- SCA from the title:
GHSA-fg8p-3m89-pwhf: Maliciou
- SCA from the title:
CVE-2026-123890: VMWare vCenter Authentication Bypass Using an Alternate Path or Channel Vulnerability added to CISA's Known Exploited Vulnerabilities catalog
Broadcom VMware vCenter contains an authentication bypass using an alternate path or channel vulnerability in the VMware Directory Service that allows an unauthenticated attacker with network access to vCenter to bypass authentication and gain unauthorized access to the system. U
GHSA-mc8w-wjhw-45x5 / CVE-2026-114516: Etherpad: Pre-auth arbitrary file read
ep_etherpad-lite >= 1.8.14, < 3.3.3 → 3.3.3
Why tagged?
- SCA from the title:
GHSA-mc8w-wjhw-45x5 / CVE-202
- SCA from the title:
GHSA-gfwj-45pc-w6r5 / CVE-2026-103033: ALTCHA: Nil-map panic (pre-verification DoS) in v1 parseServerSignature on malformed VerificationData
github.com/altcha-org/altcha-lib-go/v2 >= 2.0.0, < 2.1.0 → 2.1.0
Why tagged?
- SCA from the title:
GHSA-gfwj-45pc-w6r5 / CVE-202
- SCA from the title:
GHSA-7hvw-3c2q-45qg / CVE-2026-103025: bep/imagemeta: Unbounded memory allocation decoding PNG `zTXt` "Raw profile type iptc" chunks
github.com/bep/imagemeta < 0.17.3 → 0.17.3
Why tagged?
- SCA from the title:
GHSA-7hvw-3c2q-45qg / CVE-202
- SCA from the title:
GHSA-v6w5-38cf-pcv8 / CVE-2026-102945: Aether Project amf: panic on an unrecovered NGAP goroutine
github.com/omec-project/amf < 1.7.1-0.20260725031321-d28042aaaea0 → 1.7.1-0.20260725031321-d28042aaaea0
Why tagged?
- SCA from the title:
GHSA-v6w5-38cf-pcv8 / CVE-202
- SCA from the title:
GHSA-wgvx-x5g3-9v29 / CVE-2026-63012: baserCMS administrative API authorization bypass through session fallback
baserproject/baser-core <= 5.2.3 → 5.3.0
Why tagged?
- SCA from the title:
GHSA-wgvx-x5g3-9v29 / CVE-202
- SCA from the title:
GHSA-2pj4-v76f-wjvx / CVE-2026-62955: baserCMS: Path Traversal Bypass via realpath() in BcThemeFileService (CVE-2026-30940 Patch Bypass)
baserproject/baser-core < 5.3.0 → 5.3.0
Why tagged?
- SCA from the title:
GHSA-2pj4-v76f-wjvx / CVE-202
- Remediation from the title:
Service (CVE-2026-30940 Patch Bypass)
- SCA from the title:
GHSA-25rm-9wvm-m38v / CVE-2026-77382: falcon-rust: Discrete-Gaussian sampler runs at 2^-33 precision, far below Falcon's requirement (reference KAT vectors no longer pass)
falcon-rust <= 0.1.3 → 0.2.0
Why tagged?
- SCA from the title:
GHSA-25rm-9wvm-m38v / CVE-202
- SCA from the title:
GHSA-r7h9-qx4h-77j5 / CVE-2026-77378: Bolt ListFormatHelper SQL injection
bolt/core < 6.1.4 → 6.1.4
Why tagged?
- SCA from the title:
GHSA-r7h9-qx4h-77j5 / CVE-202
- SCA from the title:
GHSA-3xjf-9q55-vxw4 / CVE-2026-77380: Bolt: Prevent SSRF due to unchecked followed redirects
bolt/core < 6.1.5 → 6.1.5
Why tagged?
- SCA from the title:
GHSA-3xjf-9q55-vxw4 / CVE-202
- SCA from the title:
GHSA-6358-jg5p-hmjj / CVE-2026-77379: Bolt: Information disclosure through unfiltered public relation API endpoint
bolt/core < 6.1.4 → 6.1.4
Why tagged?
- SCA from the title:
GHSA-6358-jg5p-hmjj / CVE-202
- SCA from the title:
GHSA-2535-j2pq-qq4r / CVE-2026-77377: Bolt: Server-Side Request Forgery (SSRF) in URL-upload and embed endpoints
bolt/core < 6.1.4 → 6.1.4
Why tagged?
- SCA from the title:
GHSA-2535-j2pq-qq4r / CVE-202
- SCA from the title:
GHSA-xr6g-7g83-j865 / CVE-2026-77376: Bolt: Open redirect enables post-authentication redirection to arbitrary domains
bolt/core < 6.1.4 → 6.1.4
Why tagged?
- SCA from the title:
GHSA-xr6g-7g83-j865 / CVE-202
- SCA from the title:
GHSA-wj7x-58c2-5793 / CVE-2026-77369: Daptin: Broken Access Control (IDOR) in the generic YJS collaboration endpoint
github.com/daptin/daptin >= 0.11.4, < 0.12.30 → 0.12.30
Why tagged?
- SCA from the title:
GHSA-wj7x-58c2-5793 / CVE-202
- SCA from the title:
GHSA-hq2p-f2vj-v3cm / CVE-2026-77367: Daptin: Unauthenticated SQL Injection via the `sort` query parameter on every entity list endpoint
github.com/daptin/daptin <= 0.12.29 → 0.12.30
Why tagged?
- SCA from the title:
GHSA-hq2p-f2vj-v3cm / CVE-202
- SCA from the title:
GHSA-9x8x-crjq-g64h / CVE-2026-77359: Jupyter MCP Server: Browser DNS rebinding can hijack the Jupyter backend through management routes
jupyter-mcp-server <= 1.0.2 → 1.0.3
Why tagged?
- SCA from the title:
GHSA-9x8x-crjq-g64h / CVE-202
- SCA from the title:
GHSA-24pw-rf5p-mgp7 / CVE-2026-77318: Jupyter MCP Server: Unauthenticated management routes can hijack the Jupyter backend in standalone HTTP mode
jupyter-mcp-server <= 1.0.2 → 1.0.3
Why tagged?
- SCA from the title:
GHSA-24pw-rf5p-mgp7 / CVE-202
- SCA from the title:
GHSA-6pm8-6f34-9v3g / CVE-2026-77316: Flyto2 Core: SSRF guard bypass via DNS rebinding (validate_url_ssrf resolves-then-connects without pinning)
flyto-core <= 2.26.7 → 2.26.8
Why tagged?
- SCA from the title:
GHSA-6pm8-6f34-9v3g / CVE-202
- SCA from the title:
GHSA-2mr3-rxrq-238c / CVE-2026-77315: Flyto2 Core: http.paginate follows server-supplied next-page URLs (Link header / cursor) without SSRF revalidation
flyto-core <= 2.26.7 → 2.26.8
Why tagged?
- SCA from the title:
GHSA-2mr3-rxrq-238c / CVE-202
- SCA from the title:
GHSA-pfg2-w999-497v / CVE-2026-77313: Flyto2 Core: SSRF guard validates the resolved IP but connects by hostname, allowing DNS-rebinding TOCTOU
flyto-core <= 2.26.7 → 2.26.8
Why tagged?
- SCA from the title:
GHSA-pfg2-w999-497v / CVE-202
- SCA from the title:
GHSA-p34x-fmph-9fjx / CVE-2026-77312: Flyto2 Core: Arbitrary file write via unguarded data.*/file.* modules (incomplete fix of CVE-2026-67429)
flyto-core <= 2.26.7 → 2.26.8
Why tagged?
- SCA from the title:
GHSA-p34x-fmph-9fjx / CVE-202
- SCA from the title:
GHSA-86mf-q4h5-69gp / CVE-2026-59988: django-docutils unsafe Docutils defaults allow local file disclosure, SSRF, and stored XSS
django-docutils < 0.30.0 → 0.30.0
Why tagged?
- SCA from the title:
GHSA-86mf-q4h5-69gp / CVE-202
- SCA from the title:
GHSA-c3cj-3p6p-j822 / CVE-2026-63415: Jane: $ref resolution performs SSRF + LFI (path traversal) at code-generation time (jane-php)
jane-php/open-api-3 < 7.12.0 → 7.12.0
Why tagged?
- SCA from the title:
GHSA-c3cj-3p6p-j822 / CVE-202
- SCA from the title:
GHSA-p32v-8v8j-j534 / CVE-2026-63344: Refitter allows arbitrary code execution through unescaped OpenAPI content-type values
Refitter < 2.1.2 → 2.1.2
Why tagged?
- SCA from the title:
GHSA-p32v-8v8j-j534 / CVE-202
- SCA from the title:
GHSA-58x9-vjvp-6mx8 / CVE-2026-63346: Refitter allows code execution through unescaped OpenAPI header parameter names
Refitter < 2.1.2 → 2.1.2
Why tagged?
- SCA from the title:
GHSA-58x9-vjvp-6mx8 / CVE-202
- SCA from the title:
GHSA-3fhm-p725-h3g3 / CVE-2026-63345: Refitter allows arbitrary code execution through unescaped OpenAPI paths
Refitter < 2.1.2 → 2.1.2
Why tagged?
- SCA from the title:
GHSA-3fhm-p725-h3g3 / CVE-202
- SCA from the title:
GHSA-p957-7v2w-g93g / CVE-2026-58208: NATS Server: MQTT-over-WebSocket Path Can Crash WebSocket-Only JetStream Servers Before MQTT Is Enabled
github.com/nats-io/nats-server/v2 < 2.12.12 → 2.12.12 | >= 2.14.0-RC.1, < 2.14.3 → 2.14.3
Why tagged?
- SCA from the title:
GHSA-p957-7v2w-g93g / CVE-202
- SCA from the title:
GHSA-r72h-j7qq-v6qg / CVE-2026-58210: NATS Server allows unauthenticated memory exhaustion through incomplete MQTT CONNECT packets
github.com/nats-io/nats-server/v2 < 2.12.12 → 2.12.12 | >= 2.14.0-RC.1, < 2.14.3 → 2.14.3
Why tagged?
- SCA from the title:
GHSA-r72h-j7qq-v6qg / CVE-202
- SCA from the title:
GHSA-7qmq-8cc4-hxwg / CVE-2026-58209: NATS Server MQTT retained messages and QoS replay bypass subscription deny rules
github.com/nats-io/nats-server/v2 < 2.12.12 → 2.12.12 | >= 2.14.0-RC.1, < 2.14.3 → 2.14.3
Why tagged?
- SCA from the title:
GHSA-7qmq-8cc4-hxwg / CVE-202
- SCA from the title:
GHSA-x26x-7f4v-cqx7 / CVE-2026-62337: snark-verifier: Halo 2 aggregation circuit mishandles point-at-infinity proof elements
snark-verifier < 0.2.5 → 0.2.6
Why tagged?
- SCA from the title:
GHSA-x26x-7f4v-cqx7 / CVE-202
- SCA from the title:
CVE-2025-42884: SAP NetWeaver Improper Neutralization of Special Elements in Data Query Logic Vulnerability added to CISA's Known Exploited Vulnerabilities catalog
SAP NetWeaver Enterprise Portal contains an improper neutralization of special elements in data query logic vulnerability that allows an unauthenticated attacker to disclose or modify server information via injected JNDI environment properties or a URL used during JNDI lookup ope
CVE-2026-129448: Apache Roller Deserialization of Untrusted Data Vulnerability added to CISA's Known Exploited Vulnerabilities catalog
Apache Roller contains a deserialization of untrusted data vulnerability that allows an unauthenticated remote attacker to execute arbitrary code via the XML-RPC endpoint, which accepts and deserializes vendor extension types before authentication. This CVE covers the same underl
CVE-2026-76466: Cisco Expressway Series Use of Hard-coded Credentials Vulnerability added to CISA's Known Exploited Vulnerabilities catalog
Cisco Expressway Series contains a use of hard-coded credentials vulnerability that allows an unauthenticated, remote attacker with persistent cookies and network access to execute commands as root on a clustered device via the database service. US federal agencies must act by 20
GHSA-wr3g-j6qj-xpgh / CVE-2026-128135: NLTK: ZIP package extraction follows in-root hardlinks and overwrites files outside the NLTK data root
nltk >= 3.9.4, <= 3.10.3 → 3.10.4
Why tagged?
- SCA from the title:
GHSA-wr3g-j6qj-xpgh / CVE-202
- SCA from the title:
GHSA-c59x-vh6j-3w8v / CVE-2026-128136: NLTK: AllowlistUnpickler does not deny numpy submodule-local file-I/O sinks
nltk >= 3.10.0, < 3.10.4 → 3.10.4
Why tagged?
- SCA from the title:
GHSA-c59x-vh6j-3w8v / CVE-202
- SCA from the title:
GHSA-g58v-j9g9-5gfg / CVE-2026-128137: NLTK corpus-reader view methods bypass the scoped root sandbox via intermediate-directory symlinks
nltk >= 3.9.4, < 3.10.4 → 3.10.4
Why tagged?
- SCA from the title:
GHSA-g58v-j9g9-5gfg / CVE-202
- SCA from the title:
GHSA-x8q7-6c7m-52gw / CVE-2026-128138: NLTK incomplete fix: additional JVM/JAR sandbox bypass through unvalidated launcher tokens in java() command arguments
nltk >= 3.10.3, < 3.10.4 → 3.10.4
Why tagged?
- SCA from the title:
GHSA-x8q7-6c7m-52gw / CVE-202
- SCA from the title:
GHSA-j8g8-j4j7-8j54 / CVE-2026-128139: NLTK: XMLCorpusView comment and CDATA parsing permits quadratic CPU denial of service
nltk >= 3.6, <= 3.10.3 → 3.10.4
Why tagged?
- SCA from the title:
GHSA-j8g8-j4j7-8j54 / CVE-202
- SCA from the title:
GHSA-pcm8-fqjx-rvx8 / CVE-2026-128140: NLTK: Downloader cyclic collection indices cause an infinite closure walk
nltk >= 3.6.7, < 3.10.4 → 3.10.4
Why tagged?
- SCA from the title:
GHSA-pcm8-fqjx-rvx8 / CVE-202
- SCA from the title:
GHSA-9ffx-rrgx-mhgx / CVE-2026-129221: NLTK: ARFF_Formatter Injects Weka ARFF Schema Directives via Attacker-Controlled Class Labels
nltk <= 3.10.3 → 3.10.4
Why tagged?
- SCA from the title:
GHSA-9ffx-rrgx-mhgx / CVE-202
- SCA from the title:
GHSA-rh8m-wqhc-qmrf / CVE-2026-129222: Natural Language Toolkit (NLTK): Uncontrolled recursion (crash DoS) in DependencyGraph.tree()/triples()
nltk <= 3.10.3 → 3.10.4
Why tagged?
- SCA from the title:
GHSA-rh8m-wqhc-qmrf / CVE-202
- SCA from the title:
GHSA-8846-p9w9-5frf / CVE-2026-129223: Natural Language Toolkit (NLTK): Uncontrolled recursion (crash DoS) in Synset.tree()/acyclic_tree() via WordNet relation traversal
nltk <= 3.10.3 → 3.10.4
Why tagged?
- SCA from the title:
GHSA-8846-p9w9-5frf / CVE-202
- SCA from the title:
GHSA-3h95-x772-4765 / CVE-2026-129224: NLTK: Uncontrolled recursion in CCG lexicon parser causes denial of service via deeply nested category input
nltk <= 3.10.3 → 3.10.4
Why tagged?
- SCA from the title:
GHSA-3h95-x772-4765 / CVE-202
- SCA from the title:
GHSA-xfcv-m889-fmqg / CVE-2026-129225: NLTK: Uncontrolled recursion in DependencyGraph traversal causes denial of service via deep dependency chains
nltk <= 3.10.3 → 3.10.4
Why tagged?
- SCA from the title:
GHSA-xfcv-m889-fmqg / CVE-202
- SCA from the title:
GHSA-wq4f-hq55-wf9w: Malware in ct-fivem
ct-fivem >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-wq4f-hq55-wf9w: Malware
- SCA from the title:
GHSA-g682-2jxm-42xh: Malware in aciaiaggu-idat-gfda
aciaiaggu-idat-gfda = 1.1.2 → remove it
Why tagged?
- SCA from the title:
GHSA-g682-2jxm-42xh: Malware
- SCA from the title:
GHSA-p98v-v2hr-rrxr: Malware in abyil-nionai-lasuk
abyil-nionai-lasuk = 1.3.3 → remove it
Why tagged?
- SCA from the title:
GHSA-p98v-v2hr-rrxr: Malware
- SCA from the title:
GHSA-6692-fm7p-jj3q: Malware in abyil-nina-lasuk
abyil-nina-lasuk = 1.3.3 → remove it
Why tagged?
- SCA from the title:
GHSA-6692-fm7p-jj3q: Malware
- SCA from the title:
GHSA-f488-9hp8-qv8h: Malware in abyikula-nioybnali-lauykia
abyikula-nioybnali-lauykia = 1.1.3 → remove it
Why tagged?
- SCA from the title:
GHSA-f488-9hp8-qv8h: Malware
- SCA from the title:
GHSA-v56h-584w-6f7p: Malware in abukhalid
abukhalid = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-v56h-584w-6f7p: Malware
- SCA from the title:
GHSA-4gr2-c235-xq3h: Malware in abina-amugmi-amm
abina-amugmi-amm = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-4gr2-c235-xq3h: Malware
- SCA from the title:
GHSA-7h99-fgqf-hr3c: Malware in abiba-avin-aumauna
abiba-avin-aumauna = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-7h99-fgqf-hr3c: Malware
- SCA from the title:
GHSA-gm9r-hvc9-96gv / CVE-2026-129304: Guard Core: Unvalidated X-Forwarded-For-derived string used as a Redis key component and interpolated into a KEYS glob pattern
guard-core >= 1.0.0, < 3.13.0 → 3.13.0
Why tagged?
- SCA from the title:
GHSA-gm9r-hvc9-96gv / CVE-202
- SCA from the title:
GHSA-w7wg-6q7v-44f2 / CVE-2026-129303: Guard Core: Whitespace-collapse preprocessing permanently disables the CRLF-anchored http-splitting and command-injection detectors in the default detection mode
guard-core >= 1.0.0, < 3.13.0 → 3.13.0
Why tagged?
- SCA from the title:
GHSA-w7wg-6q7v-44f2 / CVE-202
- SCA from the title:
GHSA-r7hm-rjvg-xx7j / CVE-2026-129302: Guard Core: Quadratic ReDoS in built-in detection pattern freezes the event loop with a single request
guard-core >= 3.5.0, <= 3.12.0 → 3.13.0
Why tagged?
- SCA from the title:
GHSA-r7hm-rjvg-xx7j / CVE-202
- SCA from the title:
GHSA-m932-63jc-4jqq / CVE-2026-130007: k8s-mcp-server: Missing authentication on default SSE/HTTP transport allows unauthenticated Kubernetes tool execution
github.com/reza-gholizade/k8s-mcp-server < 1.1.0 → 1.1.0
Why tagged?
- SCA from the title:
GHSA-m932-63jc-4jqq / CVE-202
- AI Security from the title:
/ CVE-2026-130007: k8s-mcp-server: Missing authentication on default SSE/HTTP tra
- SCA from the title:
GHSA-3mgh-93r5-r7jf / CVE-2026-83816: CodeWhale: exec_shell parallel-readonly classifier auto-approves fd/rg/git grep exec flags enabling silent RCE
codewhale-tui <= 0.8.67 → 0.9.0; codewhale <= 0.8.67 → 0.9.0
Why tagged?
- SCA from the title:
GHSA-3mgh-93r5-r7jf / CVE-202
- SCA from the title:
GHSA-8hp3-xxrg-v9c8 / CVE-2026-83817: CodeWhale: Automation auto_approve defaults to true, bypassing the task-path hardening fix for silent recurring agent execution
codewhale-tui <= 0.8.67 → 0.9.0; codewhale <= 0.8.67 → 0.9.0
Why tagged?
- SCA from the title:
GHSA-8hp3-xxrg-v9c8 / CVE-202
- SCA from the title:
GHSA-m4g8-47f9-h588 / CVE-2026-129307: eml_parser: Algorithmic-complexity DoS (O(n^4) regex backtracking) in Received-header parsing
eml-parser <= 3.0.3 → 3.0.4
Why tagged?
- SCA from the title:
GHSA-m4g8-47f9-h588 / CVE-202
- SCA from the title:
GHSA-vwhp-8p66-mq4f / CVE-2026-95839: containerd image-triggered daemon crash via malformed digest in subject-annotated descriptor
github.com/containerd/containerd/v2 >= 2.2.0, < 2.2.10 → 2.2.10 | >= 2.3.0, < 2.3.7 → 2.3.7 | >= 2.4.0, < 2.4.2 → 2.4.2
Why tagged?
- SCA from the title:
GHSA-vwhp-8p66-mq4f / CVE-202
- SCA from the title:
GHSA-qx49-fqc8-xw99 / CVE-2026-115563: Model Context Protocol Python SDK: OAuth client could send credentials to an authorization server chosen by the MCP server
mcp >= 2.0.0a1, < 2.2.0 → 2.2.0 | >= 1.9.1, < 1.30.0 → 1.30.0
Why tagged?
- SCA from the title:
GHSA-qx49-fqc8-xw99 / CVE-202
- AI Security from the title:
OAuth client could send credentials to an authorization server chosen by the MCP server
- SCA from the title:
GHSA-phmp-hrw4-r36r / CVE-2026-97698: Mistune: Quadratic-time DoS in parse_link_href via unbounded parenthesis scan on empty-label links
mistune < 3.3.4 → 3.3.4
Why tagged?
- SCA from the title:
GHSA-phmp-hrw4-r36r / CVE-202
- SCA from the title:
GHSA-ww7q-mxrj-5ffg / CVE-2026-97699: Mistune: Quadratic-time DoS in inline image parsing (precedence_scan) bypasses not-is-image guards
mistune < 3.3.4 → 3.3.4
Why tagged?
- SCA from the title:
GHSA-ww7q-mxrj-5ffg / CVE-202
- SCA from the title:
GHSA-hj9c-qx2w-g7mh / CVE-2026-107853: tiny-secp256k1: Stale buffer after ignored wasm failure accepts invalid infinity tweak
tiny-secp256k1 >= 2.1.0, < 2.2.5 → 2.2.5; @bitcoin-js/tiny-secp256k1-asmjs >= 2.2.2, < 2.2.5 → 2.2.5
Why tagged?
- SCA from the title:
GHSA-hj9c-qx2w-g7mh / CVE-202
- SCA from the title:
GHSA-7rj6-7pqx-v7rm / CVE-2026-121717: fzf: Predictable FIFO path in zsh completion allows local symlink attack / arbitrary file overwrite as the victim user (_fzf_feed_fifo)
github.com/junegunn/fzf <= 0.74.4 → 0.74.5
Why tagged?
- SCA from the title:
GHSA-7rj6-7pqx-v7rm / CVE-202
- SCA from the title:
GHSA-w6x2-f5m4-xw82 / CVE-2026-121716: fzf: Arbitrary command execution via bash arithmetic expansion on unvalidated layout size in fzf-tmux (-l/-u attached value)
github.com/junegunn/fzf <= 0.74.4 → 0.74.5
Why tagged?
- SCA from the title:
GHSA-w6x2-f5m4-xw82 / CVE-202
- SCA from the title:
GHSA-q433-mp6c-8v4f / CVE-2026-130008: sqlite-mcp: Read-only mode bypass via statement chaining and SQL injection in describe_table
github.com/StacklokLabs/sqlite-mcp < 0.1.2 → 0.1.2
Why tagged?
- SCA from the title:
GHSA-q433-mp6c-8v4f / CVE-202
- AI Security from the title:
CVE-2026-130008: sqlite-mcp: Read-only mode bypass via statement chaining and SQL injection in describe_table
- SCA from the title:
GHSA-f3mh-rxg3-f5g2 / CVE-2026-119346: Next.js: HttpOnly cookie exposure through internal response header on Next.js Edge runtime routes
next >= 15.0.0, <= 15.5.28 → 15.5.29 | >= 16.0.0, <= 16.4.4 → 16.4.5
Why tagged?
- SCA from the title:
GHSA-f3mh-rxg3-f5g2 / CVE-202
- SCA from the title:
GHSA-7qx7-33qx-rqx2 / CVE-2026-119347: Next.js: SVG rejection bypass in the image optimization
next >= 15.0.0, <= 15.5.28 → 15.5.29 | >= 16.0.0, <= 16.4.4 → 16.4.5
Why tagged?
- SCA from the title:
GHSA-7qx7-33qx-rqx2 / CVE-202
- SCA from the title:
GHSA-pc58-hwjq-p385 / CVE-2026-119348: Next.js: Cross-client response injection and disclosure in self-hosted Next.js applications forwarding fetched responses
next >= 16.0.0, <= 16.4.4 → 16.4.5 | <= 15.5.28 → 15.5.29
Why tagged?
- SCA from the title:
GHSA-pc58-hwjq-p385 / CVE-202
- SCA from the title:
GHSA-rhh4-g77r-r9qj / CVE-2026-119349: Next.js: Cross-user cache disclosure and poisoning in Next.js use cache with binary arguments
next >= 16.0.0, <= 16.4.4 → 16.4.5
Why tagged?
- SCA from the title:
GHSA-rhh4-g77r-r9qj / CVE-202
- SCA from the title:
GHSA-vvgp-ww4w-46vf / CVE-2026-119350: Next.js: Cache poisoning of shared fallback shells in Cache Components via request-supplied placeholder route params
next >= 16.4.0, <= 16.4.4 → 16.4.5
Why tagged?
- SCA from the title:
GHSA-vvgp-ww4w-46vf / CVE-202
- SCA from the title:
GHSA-4rj4-rcrq-gr92: Safari MCP: JavaScript injection through single-quoted tool arguments (backslash not escaped)
safari-mcp < 2.22.15 → 2.22.15
Why tagged?
- SCA from the title:
GHSA-4rj4-rcrq-gr92: Safari M
- AI Security from the title:
-4rj4-rcrq-gr92: Safari MCP: JavaScript injection through single-quote
- SCA from the title:
GHSA-7589-6fvf-x4pw / CVE-2026-121707: Effect: ReDoS in Schema.TemplateLiteral compiled regex
effect <= 3.22.0 → 3.22.1
Why tagged?
- SCA from the title:
GHSA-7589-6fvf-x4pw / CVE-202
- SCA from the title:
GHSA-56v3-jrq2-4q9m / CVE-2026-77597: iSponsorBlockTV: SSRF via Malicious SSDP Response Spoofing in Local Device Discovery
iSponsorBlockTV <= 2.10.0 → 2.11.0
Why tagged?
- SCA from the title:
GHSA-56v3-jrq2-4q9m / CVE-202
- SCA from the title:
GHSA-5hj8-q7fv-qrj6 / CVE-2026-128073: gosaml2: Unauthenticated panic decrypting an EncryptedAssertion with a short or empty CipherValue
github.com/russellhaering/gosaml2 <= 0.11.0 → 0.12.0
Why tagged?
- SCA from the title:
GHSA-5hj8-q7fv-qrj6 / CVE-202
- SCA from the title:
GHSA-464h-4j8h-q5mf / CVE-2026-102529: HtmlSanitizer: CSS Removal DoS
HtmlSanitizer < 9.0.967 → 9.0.967 | >= 9.1.878-beta, < 9.1.968-beta → 9.1.968-beta
Why tagged?
- SCA from the title:
GHSA-464h-4j8h-q5mf / CVE-202
- SCA from the title:
GHSA-h5m9-42h9-vcq6 / CVE-2026-115472: Doorkeeper: When using public clients, any client can revoke any access token
doorkeeper < 5.9.1 → 5.9.1
Why tagged?
- SCA from the title:
GHSA-h5m9-42h9-vcq6 / CVE-202
- SCA from the title:
GHSA-w3w6-9m25-g88p / CVE-2026-109549: OmniFaces: SSE push channels are not bound to their owning HTTP session
org.omnifaces:omnifaces >= 5.2.0, <= 5.4.2 → 5.4.3
Why tagged?
- SCA from the title:
GHSA-w3w6-9m25-g88p / CVE-202
- SCA from the title:
GHSA-mqwx-84vv-mp26 / CVE-2026-63193: October: Media Library Crop Handler Bypasses Upload Extension Allowlist
october/october <= 3.7.13 → no fix | >= 4.0.0, <= 4.3.1 → 4.3.2 · partly fixed
Why tagged?
- SCA from the title:
GHSA-mqwx-84vv-mp26 / CVE-202
- SCA from the title:
GHSA-pxh3-4qqv-58mg / CVE-2026-61713: Servo Sandbox bypass: declarative refresh can auto-navigate a sandboxed iframe
servo < 0.3.0 → 0.3.0
Why tagged?
- SCA from the title:
GHSA-pxh3-4qqv-58mg / CVE-202
- SCA from the title:
GHSA-jmmc-wjpc-pg34 / CVE-2026-61689: XWiki Platform: HQL injection in search allows unauthenticated database extraction including password hashes
org.xwiki.platform:xwiki-platform-rest-server >= 4.3-milestone-1, < 16.10.18 → 16.10.18 | >= 18.0.0-rc-1, < 18.2.0 → 18.2.0 | >= 17.0.0-rc-1, < 17.10.5 → 17.10.5
Why tagged?
- SCA from the title:
GHSA-jmmc-wjpc-pg34 / CVE-202
- SCA from the title:
GHSA-3h63-w8jq-rrf2 / CVE-2026-59975: SharpIppNext: Unbounded IPP Document Stream Buffering Leads to Denial of Service
SharpIppNext <= 4.0.2 → 4.1.0
Why tagged?
- SCA from the title:
GHSA-3h63-w8jq-rrf2 / CVE-202
- SCA from the title:
GHSA-mx6p-3fg7-v6pj / CVE-2026-77283: obsidian-sync-mcp: Missing Host/Origin validation lets a public website drive a victim's Obsidian vault via DNS rebinding (no-auth mode)
obsidian-sync-mcp <= 0.5.6 → 0.5.7
Why tagged?
- SCA from the title:
GHSA-mx6p-3fg7-v6pj / CVE-202
- SCA from the title:
GHSA-gpcc-36pq-8qxr / CVE-2026-76090: Tapir: Construction/decode RCE via property name -> raw case-class field (tapir-openapi-codegen)
com.softwaremill.sttp.tapir:tapir-openapi-codegen-core < 1.13.27 → 1.13.27
Why tagged?
- SCA from the title:
GHSA-gpcc-36pq-8qxr / CVE-202
- SCA from the title:
GHSA-833v-v58w-294h / CVE-2026-76807: Todoist MCP Server: Browser DNS rebinding lets websites write and delete Todoist data through local MCP server
@doist/todoist-mcp <= 10.3.2 → 10.3.3
Why tagged?
- SCA from the title:
GHSA-833v-v58w-294h / CVE-202
- SCA from the title:
GHSA-w42c-h7hr-f67p / CVE-2026-62964: Gortex: Arbitrary file write / repo-confinement escape in `write_file` / `edit_file` / `move_inline` MCP tools → code execution
github.com/zzet/gortex < 0.55.0 → 0.55.0
Why tagged?
- SCA from the title:
GHSA-w42c-h7hr-f67p / CVE-202
- SCA from the title:
GHSA-4c2f-96cf-f5fc / CVE-2026-75522: OpenID4VP: X.509 chain validation accepts a forged certificate that reuses a trusted anchor's Subject DN without verifying its signature
@openeudi/openid4vp <= 0.8.0 → 0.8.1
Why tagged?
- SCA from the title:
GHSA-4c2f-96cf-f5fc / CVE-202
- SCA from the title:
GHSA-j282-pjg5-j643 / CVE-2026-76101: keystore-go: Keystore integrity and password verification bypass via stripped trailing digest in Decode()
github.com/pavel-v-chernykh/keystore-go <= 2.1.0 → no fix; github.com/pavel-v-chernykh/keystore-go/v3 < 3.0.0 → 3.0.0 · partly fixed
Why tagged?
- SCA from the title:
GHSA-j282-pjg5-j643 / CVE-202
- SCA from the title:
GHSA-r7wg-f7r2-8wf7 / CVE-2026-76818: Axon: Download of Code Without Integrity Check in axon-mcp
axon-mcp <= 0.1.0 → no fix
Why tagged?
- SCA from the title:
GHSA-r7wg-f7r2-8wf7 / CVE-202
- SCA from the title:
GHSA-7qwg-r443-84p9: Malware in vp-baileys
vp-baileys = 0.0.0-stage → remove it | = 9.0.34 → remove it
Why tagged?
- SCA from the title:
GHSA-7qwg-r443-84p9: Malware
- SCA from the title:
GHSA-f8vg-jp77-mvx4: Malware in @andrewstory18/is-real-odd
@andrewstory18/is-real-odd >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-f8vg-jp77-mvx4: Malware
- SCA from the title:
PHP Fixes 7 Critical Flaws, Including Bugs That Could Allow Remote Code Execution
The PHP Foundation has released security updates to address multiple critical security flaws that could be exploited to achieve remote code execution on affected deployments, including CVE-2026-115560. The list of vulnerabilities is as follows - CVE-2026-115560 (CVSS score:…
Why tagged?
- Remediation from the excerpt:
Foundation has released security updates to address multiple cri
- Remediation from the excerpt:
GHSA-pm45-rm93-2g47: Malware in item-validates
item-validates >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-pm45-rm93-2g47: Malware
- SCA from the title:
GHSA-59c6-w34f-h244: Malicious code in besk (crates.io)
besk = 0.1.1 → remove it
Why tagged?
- SCA from the title:
GHSA-59c6-w34f-h244: Maliciou
- SCA from the title:
GHSA-2r45-7hg7-w99r: Malware in @mibbp/agent-observer
@mibbp/agent-observer >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-2r45-7hg7-w99r: Malware
- SCA from the title:
GHSA-mf5v-3qmw-mv6q: Malware in @poucode/baileys
@poucode/baileys >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-mf5v-3qmw-mv6q: Malware
- SCA from the title:
Ruby2Shell: critical Ruby RCE, affected versions and how to fix it (GHSA-34m4-m9fh-gqp5)
Ruby2Shell is a critical Ruby flaw that can give attackers code execution. See affected versions, whether GitLab is hit, and how to upgrade and fix it. Category: Vulnerabilities & Threats
PHP security updates fix 18 flaws, including critical RCE bugs
The PHP development team released security updates addressing 18 vulnerabilities, including critical flaws that could allow unauthenticated attackers to remotely execute code on vulnerable servers. [...]
Why tagged?
- Remediation from the title:
PHP security updates fix 18 flaws, including
- Remediation from the title:
GHSA-v228-pf8g-jx8g: Malware in npmresearch2026-scope-test
npmresearch2026-scope-test >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-v228-pf8g-jx8g: Malware
- SCA from the title:
GHSA-5jcj-xh7v-92qr: Malware in scope-test-af5c5e
scope-test-af5c5e >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-5jcj-xh7v-92qr: Malware
- SCA from the title:
GHSA-rj9g-592x-g9w3: Malware in npmresearch2026-prov-test
npmresearch2026-prov-test >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-rj9g-592x-g9w3: Malware
- SCA from the title:
GHSA-6hrm-xfrq-h4qh: Malware in metrics-probe-9b4c
metrics-probe-9b4c >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-6hrm-xfrq-h4qh: Malware
- SCA from the title:
GHSA-c4v5-qmr8-hq6m: Malware in npmresearch2026-scope-test-b
npmresearch2026-scope-test-b >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-c4v5-qmr8-hq6m: Malware
- SCA from the title:
GHSA-6vvv-7q4x-wvgg: Malware in @npmresearch4/utils
@npmresearch4/utils >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-6vvv-7q4x-wvgg: Malware
- SCA from the title:
GHSA-q8v2-3j4h-xg2p / CVE-2026-63412: Jane: Instantiation RCE via query parameter name -> raw PHPDoc */ breakout (jane-php/open-api-3)
jane-php/open-api-3 < 7.12.0 → 7.12.0
Why tagged?
- SCA from the title:
GHSA-q8v2-3j4h-xg2p / CVE-202
- SCA from the title:
GHSA-x9xr-53qx-9qcf / CVE-2026-63413: Jane: Instantiation RCE via header parameter name -> raw PHPDoc */ breakout (jane-php/open-api-3)
jane-php/open-api-3 < 7.12.0 → 7.12.0
Why tagged?
- SCA from the title:
GHSA-x9xr-53qx-9qcf / CVE-202
- SCA from the title:
GHSA-xwcw-j52r-34x4 / CVE-2026-63411: Jane: Instantiation RCE via parameter description -> raw PHPDoc */ breakout (jane-php/open-api-3)
jane-php/open-api-3 < 7.12.0 → 7.12.0
Why tagged?
- SCA from the title:
GHSA-xwcw-j52r-34x4 / CVE-202
- SCA from the title:
GHSA-vg83-hcp4-5qcc / CVE-2026-75518: DOMShell: domshell_eval classified as read-tier can execute side-effecting JavaScript without --allow-write
@apireno/domshell < 2.0.8 → 2.0.8
Why tagged?
- SCA from the title:
GHSA-vg83-hcp4-5qcc / CVE-202
- SCA from the title:
GHSA-pj7p-238h-76pv / CVE-2026-69139: djangocms-moderation: Moderation comments disclosed to non-participant staff via the admin changelist
djangocms-moderation <= 2.3.0 → 2.4.0
Why tagged?
- SCA from the title:
GHSA-pj7p-238h-76pv / CVE-202
- SCA from the title:
GHSA-8776-qf3h-26r3 / CVE-2026-71535: Mareforma: Unsigned Claims Can Be Promoted to REPLICATED via Missing Signature Enforcement in Convergence Path
mareforma >= 0.3.0, < 0.3.7 → 0.3.7
Why tagged?
- SCA from the title:
GHSA-8776-qf3h-26r3 / CVE-202
- SCA from the title:
GHSA-xfq4-8hf9-5h43 / CVE-2026-71534: Mareforma: transparency_logged trusts the unsigned rekor block
mareforma >= 0.3.0, < 0.3.8 → 0.3.8
Why tagged?
- SCA from the title:
GHSA-xfq4-8hf9-5h43 / CVE-202
- SCA from the title:
GHSA-rgg9-956j-3378 / CVE-2026-71500: Mareforma: invalidated claims still promote to REPLICATED
mareforma >= 0.3.0, < 0.3.8 → 0.3.8
Why tagged?
- SCA from the title:
GHSA-rgg9-956j-3378 / CVE-202
- SCA from the title:
GHSA-hxh5-gp44-rc6p / CVE-2026-71536: Mareforma: verify_bundle never checks a per-claim signature
mareforma >= 0.3.0, < 0.3.8 → 0.3.8
Why tagged?
- SCA from the title:
GHSA-hxh5-gp44-rc6p / CVE-202
- SCA from the title:
GHSA-m29v-3g7g-9c63 / CVE-2026-71533: Mareforma: search_claims skips verify-on-read, serving forged rows
mareforma = 0.3.7 → 0.3.8
Why tagged?
- SCA from the title:
GHSA-m29v-3g7g-9c63 / CVE-202
- SCA from the title:
GHSA-4g68-3pwx-5vfj / CVE-2026-58214: NATS Server MQTT subscribe permission bypass exposes internal QoS 2 metadata
github.com/nats-io/nats-server/v2 < 2.12.12 → 2.12.12 | >= 2.14.0-RC.1, < 2.14.3 → 2.14.3
Why tagged?
- SCA from the title:
GHSA-4g68-3pwx-5vfj / CVE-202
- SCA from the title:
GHSA-qrcv-3558-gj4f / CVE-2026-58213: NATS Server: MQTT SUBSCRIBE Protocol Injection via Leaf Node/Route Forwarding allows arbitrary NATS command injection
github.com/nats-io/nats-server/v2 < 2.12.9 → 2.12.9 | >= 2.14.0-RC.1, < 2.14.1 → 2.14.1
Why tagged?
- SCA from the title:
GHSA-qrcv-3558-gj4f / CVE-202
- SCA from the title:
PHP Patches Seven Critical RCE Vulnerabilities
Successful exploitation could allow attackers to crash the worker process and execute code with the PHP worker’s privileges.
Why tagged?
- Remediation from the title:
PHP Patches Seven Critical RCE Vuln
- Remediation from the title:
GHSA-cpg3-jjwc-f9qx: Malicious code in secretlens (RubyGems)
secretlens = 1.0.1 → remove it
Why tagged?
- SCA from the title:
GHSA-cpg3-jjwc-f9qx: Maliciou
- SCA from the title:
GHSA-q9fg-wfvh-ggp3: Malicious code in flo-pro-adk (PyPI)
flo-pro-adk = 0.0.0 → remove it | = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-q9fg-wfvh-ggp3: Maliciou
- SCA from the title:
GHSA-v4vq-23qw-j3r8: Malware in developmentstelemetry
developmentstelemetry >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-v4vq-23qw-j3r8: Malware
- SCA from the title:
Drupal Patches Critical Installer Flaw That Could Give Unauthenticated Attackers Control of Sites
Under specific conditions, a critical vulnerability in Drupal core can allow an attacker without login credentials to use the built-in installer to attempt to reinstall a site. That can lead to a site takeover or remote code execution, and the project rates the vulnerable…
Why tagged?
- Remediation from the title:
Drupal Patches Critical Installer Flaw
- Remediation from the title:
GHSA-q2h4-4569-r3g5: Malware in @coframe-gtm/annotations
@coframe-gtm/annotations >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-q2h4-4569-r3g5: Malware
- SCA from the title:
GHSA-3hj5-cm6m-jpf4: Malware in yangon
yangon >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-3hj5-cm6m-jpf4: Malware
- SCA from the title:
GHSA-rcwx-2hqx-rf6q: Malware in daressalaam
daressalaam >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-rcwx-2hqx-rf6q: Malware
- SCA from the title:
GHSA-54f5-j4rj-57cc: Malware in algiers
algiers >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-54f5-j4rj-57cc: Malware
- SCA from the title:
GHSA-mjmq-62f2-6w3p: Malware in jeddah
jeddah >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-mjmq-62f2-6w3p: Malware
- SCA from the title:
GHSA-468r-9jxp-wpm5: Malware in ludhiana
ludhiana >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-468r-9jxp-wpm5: Malware
- SCA from the title:
GHSA-g77w-9vf6-gxmm: Malware in harbin
harbin >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-g77w-9vf6-gxmm: Malware
- SCA from the title:
GHSA-x48p-rqgw-jw6f: Malware in ranchi
ranchi >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-x48p-rqgw-jw6f: Malware
- SCA from the title:
GHSA-4whv-8gf3-58r7: Malware in nanjing
nanjing >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-4whv-8gf3-58r7: Malware
- SCA from the title:
GHSA-9qjw-3x59-9g8p: Malware in budapest
budapest >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-9qjw-3x59-9g8p: Malware
- SCA from the title:
GHSA-5cw2-p5pg-92c5: Malware in raipur
raipur >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-5cw2-p5pg-92c5: Malware
- SCA from the title:
GHSA-fr2v-c55r-89wm: Malware in ahmedabad
ahmedabad >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-fr2v-c55r-89wm: Malware
- SCA from the title:
GHSA-2w46-mc5m-fj42: Malware in bucharest
bucharest >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-2w46-mc5m-fj42: Malware
- SCA from the title:
GHSA-x6c6-38jv-xh6w: Malware in jabalpur
jabalpur >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-x6c6-38jv-xh6w: Malware
- SCA from the title:
GHSA-xw8h-93hj-q8wq: Malware in aurangabad
aurangabad >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-xw8h-93hj-q8wq: Malware
- SCA from the title:
GHSA-67rm-mx6j-p72g: Malware in meerut
meerut >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-67rm-mx6j-p72g: Malware
- SCA from the title:
GHSA-5x76-vjm4-f469: Malware in mysore
mysore >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-5x76-vjm4-f469: Malware
- SCA from the title:
GHSA-hg6p-gq65-grp4: Malware in dhaka
dhaka >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-hg6p-gq65-grp4: Malware
- SCA from the title:
GHSA-7hhj-hhv4-xqcr: Malware in hyderabad
hyderabad >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-7hhj-hhv4-xqcr: Malware
- SCA from the title:
GHSA-7pm8-488h-944p: Malware in malaga
malaga >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-7pm8-488h-944p: Malware
- SCA from the title:
GHSA-rw4h-xw5g-c7mq: Malware in birmingham
birmingham >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-rw4h-xw5g-c7mq: Malware
- SCA from the title:
GHSA-xjhh-6c5p-jq5j: Malware in bakersfield
bakersfield >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-xjhh-6c5p-jq5j: Malware
- SCA from the title:
GHSA-2744-9f6f-pwvj: Malware in fortworth
fortworth >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-2744-9f6f-pwvj: Malware
- SCA from the title:
GHSA-j7g4-cw2x-q3x8: Malware in sanantonio
sanantonio >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-j7g4-cw2x-q3x8: Malware
- SCA from the title:
GHSA-jfpc-fc9q-j73r: Malware in elpaso
elpaso >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-jfpc-fc9q-j73r: Malware
- SCA from the title:
GHSA-rrr2-8q34-85xx: Malware in oklahomacity
oklahomacity >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-rrr2-8q34-85xx: Malware
- SCA from the title:
GHSA-8575-5pff-xp49: Malware in tabnine
tabnine >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-8575-5pff-xp49: Malware
- SCA from the title:
GHSA-6h9x-rjf5-jw55: Malware in requester-lb
requester-lb >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-6h9x-rjf5-jw55: Malware
- SCA from the title:
GHSA-448f-g3c2-cq9v: Malware in litecore-lib-ltc
litecore-lib-ltc >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-448f-g3c2-cq9v: Malware
- SCA from the title:
GHSA-2rgp-c9mf-f8q7: Malware in @claudeorg/universal-code-generator
@claudeorg/universal-code-generator >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-2rgp-c9mf-f8q7: Malware
- SCA from the title:
GHSA-6g8w-4887-v6p3: Malware in fast-deep-thinking
fast-deep-thinking >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-6g8w-4887-v6p3: Malware
- SCA from the title:
GHSA-vw84-96h8-p9rf: Malware in tailwind-keyframe-utils
tailwind-keyframe-utils >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-vw84-96h8-p9rf: Malware
- SCA from the title:
GHSA-fwpf-2rwq-r74v: Malware in @devcorelab/postcss-animkit
@devcorelab/postcss-animkit >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-fwpf-2rwq-r74v: Malware
- SCA from the title:
Drupal patches critical RCE flaw, warns exploits may surface quickly
The Drupal Security Team has patched a critical remote code execution vulnerability that can let attackers take over vulnerable sites. [...]
Why tagged?
- Remediation from the title:
Drupal patches critical RCE flaw, warn
- Remediation from the title:
Splunk Patches Nearly 140 Flaws Across Three Core Products
The security updates resolve critical and high-severity issues leading to authentication bypass, remote code execution, and privilege escalation.
Why tagged?
- Remediation from the title:
Splunk Patches Nearly 140 Flaws Across
- Remediation from the title:
GHSA-w9cm-wm83-69r3: Malicious code in fh-skeleton-web (RubyGems)
fh-skeleton-web = 1.0.1 → remove it
Why tagged?
- SCA from the title:
GHSA-w9cm-wm83-69r3: Maliciou
- SCA from the title:
GHSA-7cj4-w2r7-x3q8: Malicious code in react-native-datepickerror (npm)
react-native-datepickerror = 99.9.1 → remove it
Why tagged?
- SCA from the title:
GHSA-7cj4-w2r7-x3q8: Maliciou
- SCA from the title:
GHSA-9h9h-w8h8-rgjm: Malicious code in tajul-avengers-cli (npm)
tajul-avengers-cli = 1.4.1 → remove it
Why tagged?
- SCA from the title:
GHSA-9h9h-w8h8-rgjm: Maliciou
- SCA from the title:
GHSA-v4jp-52hh-9chp: Malicious code in calkyippie (npm)
calkyippie = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-v4jp-52hh-9chp: Maliciou
- SCA from the title:
GHSA-5f9p-65w4-73v8: Malicious code in char-ai-sdk (npm)
char-ai-sdk = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-5f9p-65w4-73v8: Maliciou
- SCA from the title:
GHSA-v32q-85mq-fg78: Malicious code in @lasha_lasha/helper (npm)
@lasha_lasha/helper = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-v32q-85mq-fg78: Maliciou
- SCA from the title:
GHSA-c7gv-mp6p-m8mj: Malicious code in calcultimatetest (npm)
calcultimatetest = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-c7gv-mp6p-m8mj: Maliciou
- SCA from the title:
GHSA-5fv6-9w6w-23xh: Malicious code in @h1stealthy/gh046-npm-transfer-9421a2 (npm)
@h1stealthy/gh046-npm-transfer-9421a2 = 0.0.386387 → remove it | = 0.0.386388 → remove it | = 0.0.95891 → remove it
Why tagged?
- SCA from the title:
GHSA-5fv6-9w6w-23xh: Maliciou
- SCA from the title:
GHSA-9599-44wr-v635: Malicious code in calcurender (npm)
calcurender = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-9599-44wr-v635: Maliciou
- SCA from the title:
GHSA-5f96-rfmm-87m9: Malicious code in character-ai-sdk (npm)
character-ai-sdk = 1.0.1 → remove it | = 1.0.0 → remove it
Why tagged?
- SCA from the title:
GHSA-5f96-rfmm-87m9: Maliciou
- SCA from the title:
GHSA-jqg3-3r6r-54f3: Malicious code in @clikwraps/navigate (npm)
@clikwraps/navigate = 99.9.1 → remove it
Why tagged?
- SCA from the title:
GHSA-jqg3-3r6r-54f3: Maliciou
- SCA from the title:
GHSA-q32v-qm2p-gw4w: Malicious code in @basis-theory-elements/api-client (npm)
@basis-theory-elements/api-client = 99.9.1 → remove it
Why tagged?
- SCA from the title:
GHSA-q32v-qm2p-gw4w: Maliciou
- SCA from the title:
GHSA-93rp-j336-vgfm: Malicious code in gmo-payment-carrier (RubyGems)
gmo-payment-carrier = 0.0.99 → remove it
Why tagged?
- SCA from the title:
GHSA-93rp-j336-vgfm: Maliciou
- SCA from the title:
GHSA-6c5q-63v2-x3j2: Malicious code in gmo-payment (RubyGems)
gmo-payment = 0.0.99 → remove it
Why tagged?
- SCA from the title:
GHSA-6c5q-63v2-x3j2: Maliciou
- SCA from the title:
GHSA-37qj-58qv-vjrv: Malicious code in aws_sdk_wrapper (RubyGems)
aws_sdk_wrapper = 0.0.99 → remove it
Why tagged?
- SCA from the title:
GHSA-37qj-58qv-vjrv: Maliciou
- SCA from the title:
CISA Warns of 4 Exploited Flaws Linked to Ransomware, Cryptomining, and LLMjacking Attacks
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added four vulnerabilities impacting Synology DiskStation Manager (DSM), BerriAI LiteLLM, Apache Axis, and Vanderbilt University Research Electronic Data Capture (REDCap) to its Known Exploited…
Why tagged?
- AI Security from the title:
ware, Cryptomining, and LLMjacking Attacks
- AI Security from the title:
PHP Readies Critical Security Updates to Patch Another RCE Flaw
Affecting the session upload progress, CVE-2026-115560 was publicly disclosed two days after PHP2Shell patches landed.
Why tagged?
- Remediation from the title:
cal Security Updates to Patch Another RCE Flaw
- Remediation from the title:
GHSA-m5xq-h2p4-962g: Malicious code in @fdcasj_dfew/md-doc-mcp (npm)
@fdcasj_dfew/md-doc-mcp = 1.0.0 → remove it | = 1.0.1 → remove it
Why tagged?
- SCA from the title:
GHSA-m5xq-h2p4-962g: Maliciou
- AI Security from the title:
GHSA-m5xq-h2p4-962g: Malicious code in @fdcasj_dfew/md-doc-mcp (npm)
- SCA from the title:
GHSA-mg93-rcxj-ghw9: Malware in nectarinei-notthedevs
nectarinei-notthedevs >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-mg93-rcxj-ghw9: Malware
- SCA from the title:
GHSA-qqhv-vvqf-75jp: Malware in kiwimflolb-notthedevs
kiwimflolb-notthedevs >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-qqhv-vvqf-75jp: Malware
- SCA from the title:
GHSA-5mc9-4q86-fv9c: Malware in raspberryf-notthedevs
raspberryf-notthedevs >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-5mc9-4q86-fv9c: Malware
- SCA from the title:
GHSA-794v-8p7x-wpvf: Malware in nectarine4-notthedevs
nectarine4-notthedevs >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-794v-8p7x-wpvf: Malware
- SCA from the title:
GHSA-mmxj-fv6x-r4hx: Malware in strawberry-notthedevs
strawberry-notthedevs >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-mmxj-fv6x-r4hx: Malware
- SCA from the title:
GHSA-phxh-49fh-gxhm: Malware in lemono0geg-notthedevs
lemono0geg-notthedevs >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-phxh-49fh-gxhm: Malware
- SCA from the title:
GHSA-hfgp-23qj-7vxf: Malware in mangodjbgd-notthedevs
mangodjbgd-notthedevs >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-hfgp-23qj-7vxf: Malware
- SCA from the title:
GHSA-m7r5-qm6f-c6q7: Malware in pearx93qja-notthedevs
pearx93qja-notthedevs >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-m7r5-qm6f-c6q7: Malware
- SCA from the title:
GHSA-v2qf-6ffc-j86r: Malware in coconutb0o-notthedevs
coconutb0o-notthedevs >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-v2qf-6ffc-j86r: Malware
- SCA from the title:
GHSA-2wm4-8qqx-958f: Malware in pearmwr0w0-notthedevs
pearmwr0w0-notthedevs >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-2wm4-8qqx-958f: Malware
- SCA from the title:
GHSA-6m66-5gxq-w93m: Malware in crypapiapi
crypapiapi >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-6m66-5gxq-w93m: Malware
- SCA from the title:
GHSA-8hw9-ch78-32cg: Malware in ruby-baileys
ruby-baileys = 0.0.0-stage → remove it | = 1.5.17 → remove it | = 1.5.18 → remove it
Why tagged?
- SCA from the title:
GHSA-8hw9-ch78-32cg: Malware
- SCA from the title:
GHSA-fj3h-g2vc-3fvx: Malware in ndraawzz-baileys
ndraawzz-baileys >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-fj3h-g2vc-3fvx: Malware
- SCA from the title:
GHSA-m4p3-qr69-gqjp: Malware in kevinx-baileys
kevinx-baileys >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-m4p3-qr69-gqjp: Malware
- SCA from the title:
GHSA-69p8-fqvj-5jw8: Malware in itssofc
itssofc >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-69p8-fqvj-5jw8: Malware
- SCA from the title:
GHSA-w5vj-vh52-62wh: Malware in aemeath-baileys
aemeath-baileys >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-w5vj-vh52-62wh: Malware
- SCA from the title:
GHSA-8gjx-j92q-wfwr: Malware in aemath
aemath >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-8gjx-j92q-wfwr: Malware
- SCA from the title:
GHSA-r483-947g-9m35: Malware in @zaxius/baileys
@zaxius/baileys >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-r483-947g-9m35: Malware
- SCA from the title:
GHSA-x6g3-r8x5-pjg4: Malware in @wanzforme/bails4u
@wanzforme/bails4u >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-x6g3-r8x5-pjg4: Malware
- SCA from the title:
GHSA-wpq7-r76p-73cp: Malware in @wanzforme/bails
@wanzforme/bails >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-wpq7-r76p-73cp: Malware
- SCA from the title:
GHSA-g3g2-5252-hcj5: Malware in @raffnotdev/baileys
@raffnotdev/baileys >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-g3g2-5252-hcj5: Malware
- SCA from the title:
GHSA-93hx-h37m-r69f: Malware in @monze1239/baileys
@monze1239/baileys >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-93hx-h37m-r69f: Malware
- SCA from the title:
GHSA-wrhf-54qp-qr2j: Malware in @lekzoz/baileys
@lekzoz/baileys >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-wrhf-54qp-qr2j: Malware
- SCA from the title:
GHSA-cmxr-cgpv-4696: Malware in @lekzsync/baileys
@lekzsync/baileys >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-cmxr-cgpv-4696: Malware
- SCA from the title:
GHSA-2q5q-m7xg-cp3v: Malware in amlekzo
amlekzo >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-2q5q-m7xg-cp3v: Malware
- SCA from the title:
GHSA-5xfm-j5g3-qrw5: Malware in @lekzox/baileys
@lekzox/baileys >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-5xfm-j5g3-qrw5: Malware
- SCA from the title:
GHSA-gvq9-v7r2-592g: Malware in @dyllxnn/baileys
@dyllxnn/baileys >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-gvq9-v7r2-592g: Malware
- SCA from the title:
GHSA-4wq5-r4mr-w74h: Malware in @bellaxchan/eleventech
@bellaxchan/eleventech >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-4wq5-r4mr-w74h: Malware
- SCA from the title:
GHSA-q8vw-5727-f25r: Malware in @bellaxchan/baileys
@bellaxchan/baileys >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-q8vw-5727-f25r: Malware
- SCA from the title:
GHSA-h7r5-j6rq-3x29: Malware in @bellaxchan/sixtech
@bellaxchan/sixtech >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-h7r5-j6rq-3x29: Malware
- SCA from the title:
GHSA-jxq3-wr67-vjq2: Malware in @bellaxchan/wbails
@bellaxchan/wbails >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-jxq3-wr67-vjq2: Malware
- SCA from the title:
GHSA-3mjw-7x59-6gr6: Malware in @bellaxchan/bellaxtech
@bellaxchan/bellaxtech >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-3mjw-7x59-6gr6: Malware
- SCA from the title:
GHSA-p99r-cq2r-f4rv: Malware in @bellaxchan/wabails
@bellaxchan/wabails >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-p99r-cq2r-f4rv: Malware
- SCA from the title:
GHSA-7rqm-pfqg-88c9: Malware in @bellaxchan/techxatz
@bellaxchan/techxatz >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-7rqm-pfqg-88c9: Malware
- SCA from the title:
GHSA-g5g9-r3pg-wm8w: Malware in @bellaxchan/beltech
@bellaxchan/beltech >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-g5g9-r3pg-wm8w: Malware
- SCA from the title:
GHSA-q695-p99r-xwj7: Malware in @bellaxchan/libsignal-node
@bellaxchan/libsignal-node >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-q695-p99r-xwj7: Malware
- SCA from the title:
GHSA-p64q-pg36-qghw: Malware in @bellaxchan/bailtech
@bellaxchan/bailtech >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-p64q-pg36-qghw: Malware
- SCA from the title:
GHSA-xmvq-9f29-fx3w: Malware in @denzz221/baileys
@denzz221/baileys >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-xmvq-9f29-fx3w: Malware
- SCA from the title:
GHSA-ffr4-pggp-r7cv: Malware in @axo_cuy/baileys
@axo_cuy/baileys >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-ffr4-pggp-r7cv: Malware
- SCA from the title:
GHSA-8h3c-p8q4-6cxp: Malware in @axo_cuy/baileyss
@axo_cuy/baileyss >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-8h3c-p8q4-6cxp: Malware
- SCA from the title:
php2shell: Assessing Elastic detection coverage relevant to CVE-2026-109618 and CVE-2026-109619
CVE-2026-109618 and CVE-2026-109619 are critical PHP core RCE flaws that leaked ahead of disclosure. We cover what is verified, why exploitation converges on a web server spawning a shell, and the Elastic detections developed to catch this behavior.
Why tagged?
- Remediation from the excerpt:
sclosure and before any patch existed. The PHP securi
- Remediation from the excerpt:
GHSA-82w4-rgrf-57v2: Malware in @nuri.yavuz.tr.2/my-unique-pinger
@nuri.yavuz.tr.2/my-unique-pinger >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-82w4-rgrf-57v2: Malware
- SCA from the title:
GHSA-66p6-67hr-9hw7: Malware in requestcatcher-pinger-v2
requestcatcher-pinger-v2 >= 0 → remove it
Why tagged?
- SCA from the title:
GHSA-66p6-67hr-9hw7: Malware
- SCA from the title:


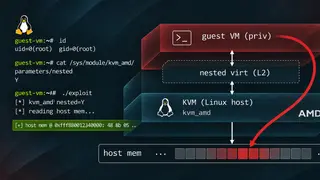
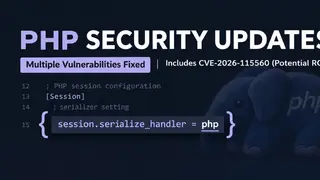
· showing 400 of 947 rows (947 developments)