Keryn HeadlinesDaily, Saturday 21 November 2026 · No. 5 · Covers 20 November 2026 00:00 to 21 November 2026 00:00 UTC |
From the editorIf you run F5 BIG-IP, F5 has released emergency patches and warns customers to patch five critical vulnerabilities that attackers can exploit for denial-of-service or remote code execution 2. Our sources name no fixed build, so take build numbers from F5's own advisory before you patch. If you run PHP with its default session handler, Cloudflare says the phpAfterShell flaw can lead to code execution 3. Cloudflare says its WAF blocks it for all customers, including Free plans, and adds rules for other PHP flaws that the same PHP release fixes 3. Our sources do not name that release, so find it and upgrade rather than rely on the WAF alone. If you still run SonicWall Generation 6 firewalls, SonicWall says they will not get security patches, even for critical flaws 5. It urges customers to retire them immediately and stop exposing them on the internet edge, citing risks from AI-assisted attacks 5. Until you replace them, we suggest you treat any internet-facing Gen 6 device as unpatchable. AI-drafted. Not reviewed by a human editor: it passed automated checks only. Published by Keryn. Corrections: keryn@keryn.dev |
Top developments |
 Amazon says Chinese hackers used Cairn AI tool to discover apparent zero-day during attack on universityThe Record · Incident · AI Security |
 F5 releases emergency patches for critical BIG-IP RCE flawsBleepingComputer · Advisory · Remediation |
 How Cloudflare WAF helps protect against phpAfterShell and other critical PHP flawsCloudflare: Security · Advisory · Remediation |
Remediation |
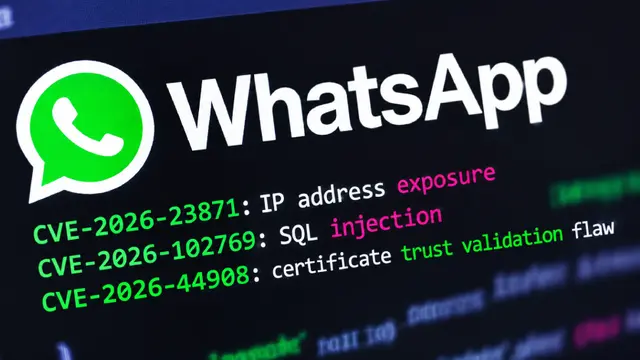 WhatsApp Patches 3 Security Flaws, Including Android Bug Suspected of Use in ScamsThe Hacker News · Advisory · Remediation |
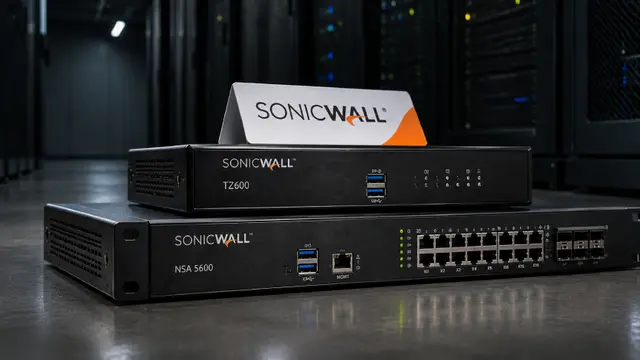 SonicWall Warns Gen 6 Firewalls Won't Get Security Patches, Even for Critical FlawsThe Hacker News · Advisory · Remediation |
AI Security |
 Your AI red team may be finding the same prompt injection thousands of timesHelp Net Security · Research · AI Security |
 AI agent API security hasn’t caught up with agents already running in productionHelp Net Security · Research · AI Security |
Advisories in this window
|
Titles, links and short excerpts only; every item links to its source. Selection is automatic; the editor's note is AI-drafted and checked as described. Preview: the unsubscribe link and Keryn's postal address are added to each email when it is sent. |