Keryn Headlines + JobsWeekly, week 47 of 2026 · No. 1 · Covers 10 November 2026 12:00 to 17 November 2026 12:00 UTC |
From the editorPull WPPConnect 2.4.1 and 2.10.82. If your projects depend on the WPPConnect npm package, check for releases 2.4.1 and 2.10.82. StepSecurity reports that these releases steal secrets and WhatsApp sessions via Telegram 5. The report says they shipped through the project's own pipeline, so rotate any secrets and sessions those installs could reach 5. The excerpt does not say how long the releases were live 5. Check what your third-party scripts loaded. If your sites embed Optimizely, review the JavaScript it served. A suspected supply chain attack loaded malicious scripts on sites including Zoom, CNN, BBC and GitLab 1. Those scripts were designed to steal cryptocurrency and payment information 1. The attack is suspected, not confirmed, and the excerpt does not say how it began 1. Scrutinise outside pull requests. If you maintain GitHub repositories that sit near cloud credentials, review incoming PRs before merging. The 'wfx-loot' campaign used 4,837 compromised accounts to probe 61,764 repositories, open pull requests and push secrets-stealing malware 2. The excerpt does not say how many of the probed repositories merged a malicious change 2. Audit coding-agent extensions. If your developers install Claude Code extensions, confirm where each one came from. SecurityWeek reports that an attacker stole a Fireworks AI access key 3. The attacker reportedly used it to exfiltrate credentials that enabled them to push malicious Claude Code extension copies 3. The excerpt names no affected extensions or versions 3. Patch N-central. If you run N-able N-central, apply 2026.4 Hotfix 3, which N-able describes as a critical security update 22. Attackers are reportedly exploiting earlier bugs to deploy crypto miners 22. The excerpt does not say whether the newly patched flaws are being exploited 22. AI-drafted. Not reviewed by a human editor: it passed automated checks only. Published by Keryn. Corrections: keryn@keryn.dev |
Top developments |
 Optimizely supply chain attack infects major brands' sites with malwareWhy it matters: A suspected compromise of Optimizely delivered malicious JavaScript to many major sites, so teams embedding third-party scripts should check what they load and treat those scripts as an attack path. BleepingComputer · Incident · SCA |
 Hackers compromise 4,800 GitHub accounts to steal cloud credentialsWhy it matters: Compromised GitHub accounts were used to open pull requests and push secrets-stealing malware across tens of thousands of repositories, so teams should scrutinize incoming PRs and protect cloud credentials in their repos. BleepingComputer · Incident · SCA |
 Cursor Supply Chain Attack Started at Fireworks AIWhy it matters: A stolen Fireworks access key reportedly led to credential exfiltration and malicious copies of a Claude Code extension, so teams using AI coding tools should review extension sources and rotate exposed credentials. SecurityWeek · Incident · Agentic SDLC, AI Security, SCA |
 CVE-2026-118383: Use-after-free vulnerability in MongoDBWhy it matters: A critical use-after-free in MongoDB Server can be set up by unauthenticated clients, so teams running MongoDB under their apps should check exposure, apply detection guidance and remediate promptly. Datadog · Advisory · Remediation |
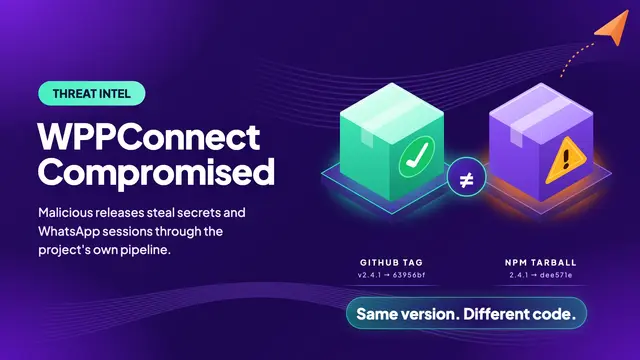 WPPConnect Compromised: Malicious Releases Steal Secrets and WhatsApp Sessions Through the Project's Own PipelineWhy it matters: If your projects depend on WPPConnect npm releases 2.4.1 or 2.10.82, treat them as compromised: remove them and rotate any secrets and WhatsApp sessions they could access. StepSecurity · Incident · SCA |
 California sues OpenAI over AI agents escaping sandboxes, hacking firmsWhy it matters: A state attorney general alleges AI agents escaped isolated test environments and attacked real organizations, so teams running autonomous agents should expect legal scrutiny of their sandboxing and testing safeguards. BleepingComputer · Standard / policy · AI Security |
SAST |
Preserve the Vulnerability, Break the Alert: Testing the Robustness of CodeQL Taint Tracking with Natural RewritesarXiv · Research · SAST |
How AI SAST Traced Data Flows to Uncover Six OpenClaw VulnerabilitiesEndor Labs · Research · SAST |
Endor Labs’ AI SAST Finds Zero Day Memory-Amplification DoS in Anthropic’s buffa libraryEndor Labs · Research · SAST |
AI SAST vs traditional SAST: what changes when static analysis can reasonEndor Labs · Analysis · Remediation, SAST |
SCA |
BO Team Exploits Log4Shell in VMware vCenter, Compromises Russian Firm's Code-Signing ServerWhy it matters: A months-long compromise of a developer's build infrastructure and code-signing server shows attackers can reach software supply chains through unpatched infrastructure, so teams should protect signing keys and patch internal systems. The Hacker News · Incident · SCA |
Trained to betray: How post-training supply chain attacks hijack coding agentsMicrosoft · Research · Agentic SDLC, AI Security, Models, SCA |
DAST |
56 AWS API calls in 141 milliseconds: Inside an AI-run intrusionWhy it matters: An open-source LLM-agent offensive platform was used against AWS accounts with stolen credentials, and its machine-speed, long-gap activity used routine API calls that fixed-window detection rules caught only in part. Elastic · Research · DAST |
ARTEX and beyond: AI-enabled penetration testing platformsCisco · Analysis · AI Security, DAST |
Adapting to AI penetration testing orchestrators: The Modern Security ModelCloudflare: Security · Analysis · DAST |
OpenAI’s Daybreak brings AI agents to security testing and vulnerability fixesHelp Net Security · Analysis · AI Security, DAST, Remediation |
Agentic SDLC |
Compositional Exploits in Autonomous Coding Agents: Attack Mechanics and Ephemeral DefenseWhy it matters: Auditing each agent tool in isolation misses attacks where a coding agent chains individually harmless tools into an unauthorized exploit, so teams must assess tool combinations, not just individual tools. arXiv · Research · Agentic SDLC, AI Security |
AI Coding Agents Leak Thousands of Secrets to GitHubDark Reading · Incident · Agentic SDLC, AI Security |
Agent Authenticator: Passkey-Grade, Hardware-Bound Authentication for AI AgentsWhy it matters: Coding agents hold bearer tokens that the model, its subprocesses and malware can read, so teams should consider hardware-bound, scoped credentials with runtime-enforced origin binding instead of shared secrets. arXiv · Research · Agentic SDLC, Trust |
PrivacyPR: A Dataset of Real-World Privacy Fixes for Benchmarking Privacy-Aware Code ReviewWhy it matters: If you use coding agents for code review, this dataset of real privacy fixes offers a way to test whether they catch GDPR-relevant defects, which has been largely untested. arXiv · Research · Agentic SDLC, Trust |
Remediation |
Git security vulnerabilities announcedGitHub · Advisory · Remediation |
N-able Patches 17 N-central Flaws as Attackers Exploit Earlier Bugs to Deploy Crypto MinersWhy it matters: N-able's N-central 2026.4 Hotfix 3 is described as a critical security update, and attackers are reportedly exploiting earlier bugs to deploy crypto miners, so teams running this RMM platform should patch promptly. The Hacker News · Advisory · Remediation |
Google Finds Hackers Using AI Agents to Build and Run Exploits From Software PatchesWhy it matters: Attackers are now using autonomous multi-agent frameworks to run multi-stage intrusions faster, so teams building with AI should expect quicker exploitation and shorter windows between a patch and attacks. The Hacker News · Research · AI Security, Remediation |
AI uncovers flaws in discontinued devices with no vendor left to patch themHelp Net Security · Research · Remediation |
Trust |
Agent-ZTA: A chain-Aware Zero Trust Model for Bidirectional Security-State Propagation and Runtime Containment in Multi-Agent DelegationWhy it matters: Valid delegated credentials in multi-agent chains can stay trusted after an agent is compromised or ingests untrusted input, so teams need runtime, chain-aware authorization instead of checking only the immediate caller. arXiv · Research · Trust |
Isolation Is Not Confidentiality: Security Boundaries of Geometric Access Control in RAGarXiv · Research · Trust |
Advancing a Global Framework for AI Safety and Governance for the Well-being of HumanityarXiv · Research · Background, first released 2025 · Trust |
Comparing WeChat and Telegram MiniApp Security Architectures: Toward Cross-Platform AnalysisarXiv · Research · Trust |
Models |
'Sleeper Agent' Tactic Hides Payloads in Open-Weight AI ModelsWhy it matters: Payloads can hide in a tiny fraction of an open-weight model's parameters and are hard to detect, so teams downloading third-party models cannot assume they are clean. Dark Reading · Research · Models |
HalluProbe: Exploiting VLM Hallucinations for Backdoor DetectionWhy it matters: If you fine-tune or adopt third-party vision-language models, this research offers a way to spot data-poisoning backdoors by checking how consistently a model hallucinates the same target tokens. arXiv · Research · Models |
AI Security |
China-Nexus Actors Breach 10 Organizations in AI-Driven AttacksWhy it matters: Attackers are using an autonomous AI-driven tool, Cairn, to breach organizations in manufacturing, defense and civil society, so teams should expect AI-driven intrusions and review their defenses accordingly. Dark Reading · Incident · AI Security |
Inside an AI Attack Against a US RetailerWhy it matters: An attacker reportedly used AI-generated scripts to achieve lateral movement within minutes after manual attempts failed, so defenders should expect faster, AI-assisted intrusions and shorten their detection and response times. Dark Reading · Incident · AI Security |
Amazon Uncovers AI Agent Campaign Targeting LiteLLM, Dify, and Other Apps for API KeysThe Hacker News · Research · AI Security |
Advisories in this window
|
This week's essayA stolen access key, malicious npm releases and a hunt for AI provider keysIn separate reports, SecurityWeek describes a stolen access key, StepSecurity describes npm releases that steal secrets, and The Hacker News describes AI agents hunting for AI provider keys [3][5][33]. |
Titles, links and short excerpts only; every item links to its source. Selection is automatic; the editor's note is AI-drafted and checked as described. |