DAST
Dynamic testing: probing running apps and APIs, fuzzing, pentest automation.
- 0 last 24h
- 10 last 7 days
- 44 in view
- RSS
Aikido launches agentic pentesting for iOS apps
Aikido now pentests iOS apps. Test your iOS and Android apps and the backend they share in one whitebox AI pentest, with AutoFix and retests. Category: Company Updates
Why tagged?
- DAST from the title:
Aikido launches agentic pentesting for iOS apps
- DAST from the title:
BackBox Linux 10 brings new hacking tools and Ubuntu 26.04 support
BackBox Linux is a free, open source penetration testing distribution made by BackBox, a non-profit community project that keeps its own repositories of ethical hacking tools. On November 19 the project released version 10, codenamed Resolute Raccoon. It’s built for…
Why tagged?
- DAST from the excerpt:
is a free, open source penetration testing distribution made by
- DAST from the excerpt:
ALIoTh: Orchestrating Multi-Agent LLMs for Autonomous IoT Penetration Testing
Penetration testing in Internet of Things (IoT) environments, especially those composed of various different devices, e.g., smart plugs, smart cameras, and smart doors, presents great challenges across the phases of information gathering, attack surface enumeration, privilege…
Why tagged?
- DAST from the title:
LLMs for Autonomous IoT Penetration Testing
- DAST from the title:
php2shell: Assessing Elastic detection coverage relevant to CVE-2026-109618 and CVE-2026-109619
CVE-2026-109618 and CVE-2026-109619 are critical PHP core RCE flaws that leaked ahead of disclosure. We cover what is verified, why exploitation converges on a web server spawning a shell, and the Elastic detections developed to catch this behavior.
Why tagged?
- Remediation from the excerpt:
sclosure and before any patch existed. The PHP securi
- Remediation from the excerpt:
Detecting Vulnerable nginx Servers with ZAP
NGINX2Root is a set of five nginx vulnerabilities which can take an attacker from a visitor to root on the server host. ZAP’s passive scanning can now flag nginx versions affected by them, and Apache HTTP Server gets the same treatment.
Why tagged?
- DAST from the title:
ulnerable nginx Servers with ZAP
- DAST from the title:
Criminals Have a New Favorite ‘Point-and-Shoot’ AI Hacking Tool
Artex and similar penetration testing tools allow newbie hackers to scan targeted systems for vulnerabilities and successfully wage attacks using prompts fed to chatbots.
Why tagged?
- DAST from the excerpt:
Artex and similar penetration testing tools allow newbie h
- DAST from the excerpt:
AI Pentesting Checklist for Web Apps: 15 Questions to Ask Before Choosing a Vendor
TL;DR Attackers move first. On average, exploitation now starts before a patch exists (Mandiant M-Trends 2026). In 1H 2026, 23% of vulnerabilities VulnCheck added to its exploited list were hit on or before disclosure day. AI pentesting vendors aren't interchangeable. Most look…
Why tagged?
- DAST from the title:
AI Pentesting Checklist for Web Ap
- DAST from the title:
Quality Isn’t The Main Worry About AI Pentesting — Data Privacy and Production Safety Are
AI is speeding up how software is built, which means more code, more changes, and more chances for vulnerabilities to reach production. It's speeding up how attackers find and exploit them too, with time-to-exploit now down to a single day. Security testing has to keep up with…
Why tagged?
- DAST from the title:
The Main Worry About AI Pentesting — Data Privacy and P
- DAST from the title:
When Do Decision Models Help LLM-Driven Network Discovery?
Network discovery, the identification of live hosts and their exposed services, is the first phase of every penetration test, and it is increasingly automated by harnesses driven by large language models (LLMs). To mitigate hallucinated or unsafe commands, recent work proposes…
Why tagged?
- DAST from the excerpt:
he first phase of every penetration test, and it is increasingly
- DAST from the excerpt:
ConnectSecure brings adaptive AI testing to vulnerability management
ConnectSecure has announced Agentic AI Penetration Testing, a new capability designed to help managed service providers (MSPs) and enterprise security teams better understand which vulnerabilities may be exploitable and require the most immediate attention. Security teams have…
Why tagged?
- DAST from the excerpt:
as announced Agentic AI Penetration Testing, a new capability de
- Remediation from the title:
adaptive AI testing to vulnerability management
- DAST from the excerpt:
ARTEX and beyond: AI-enabled penetration testing platforms
AI-enabled penetration testing and red team frameworks can automate and chain reconnaissance, vulnerability testing, and follow-on actions, lowering the skill threshold for attackers and accelerating intrusions when the tools are misused.
Why tagged?
- DAST from the title:
and beyond: AI-enabled penetration testing platforms
- AI Security from the title:
ARTEX and beyond: AI-enabled penetration testing platforms
- DAST from the title:
Adapting to AI penetration testing orchestrators: The Modern Security Model
AI-orchestrated penetration testing platforms like ARTEX have become increasingly powerful tools enabling effective attacks on exposed infrastructure. Here we share Cloudflare’s observations and recommended countermeasures.
Why tagged?
- DAST from the title:
Adapting to AI penetration testing orchestrators: The M
- DAST from the title:
Evaluating Feedback-Driven Black-Box Processes via Stochastic Modeling and Simulation
We study feedback-driven black-box processes across software engineering and machine learning. These processes are inherently sequential: policies generate inputs, observe outputs/feedback from systems, and use the feedback to guide the design of subsequent inputs. While many…
Why tagged?
- DAST from the excerpt:
ework in mutation-based fuzzing (widely used for discov
- DAST from the excerpt:
OpenAI’s Daybreak brings AI agents to security testing and vulnerability fixes
OpenAI is bringing AI agents into more of the software security process with Daybreak, pairing web application penetration testing with tools that investigate vulnerabilities and develop fixes. The two offerings, Red Team and Defense Factory, connect the work of finding…
Why tagged?
- DAST from the excerpt:
pairing web application penetration testing with tools that inve
- Remediation from the excerpt:
ecurity weaknesses with patching and retesting them. Red
- DAST from the excerpt:
Top AI network and infrastructure pentesting tools in 2026
Compare six AI network and infrastructure pentesting tools. Aikido Security is our pick for external network pentesting; see what fits internal networks. Category: DevSec Tools & Comparisons
Why tagged?
- DAST from the title:
work and infrastructure pentesting tools in 2026
- DAST from the title:
Nuclei Templates releases Nuclei Templates v10.5.2 - Release Notes
New Templates Added: 121 | CVEs Added: 102 | First-time contributions: 18 🔥 Release Highlights 🔥 [CVE-2026-123488] Craft CMS < 4.18.9, < 5.11.2 - Unauthenticated SQL Injection (@0x_Akoko) [critical] (vKEV) 🔥 [CVE-2026-123158] SSHole - OpenSSH/musl Password Auth Bypass…
Why tagged?
- DAST from the title:
Nuclei Templates releases Nucl
- DAST from the title:
Introducing ProtoSpector: A Burp Suite Extension for Analyzing, Tampering With, and Testing Protobuf and gRPC Traffic
Testing protocol buffers over HTTP can be a notoriously tedious process. Today, we’re excited to announce ProtoSpector , a Burp Suite extension designed to seamlessly decode and encode Protocol Buffer messages on the fly. By eliminating the need to constantly switch to external…
Why tagged?
- DAST from the title:
oducing ProtoSpector: A Burp Suite Extension for Ana
- DAST from the title:
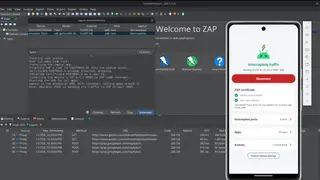
Intercepting all Android traffic with ZAP
zaptun is a community add-on by David Araújo that captures all of the traffic from an Android emulator or rooted device in ZAP with one click. It uses a VPN rather than a proxy, so apps that ignore the system proxy can’t hide from you. Here’s how it works.
Why tagged?
- DAST from the title:
ing all Android traffic with ZAP
- DAST from the title:
From Formal Methods to Fuzzing and Back
For the first twelve years of my career in computer science I mainly worked on formal methods. I had been drawn to the field as an undergraduate by its promise of a way to build software with strong, mathematically based correctness guarantees. But after many years of…
Why tagged?
- DAST from the excerpt:
from formal methods to fuzzing, by way of the GPUVerif
- DAST from the excerpt:
Wake 5: A Python Framework for Solidity Testing, Fuzzing, and Static Analysis
Smart-contract fuzzers differ by an order of magnitude in throughput and by design in how they construct inputs, yet published comparisons rarely separate the two. We present Wake 5, an open-source Python framework for Solidity testing, fuzzing and static analysis, and use it…
Why tagged?
- DAST from the excerpt:
Smart-contract fuzzers differ by an order of m
- DAST from the excerpt:
Making HTTP header injection critical with one prompt
You can now escalate HTTP header injection to a CRLF-Powered Desync and exploit it to serve random users a redirect to your collaborator, in a single prompt. We’ve just introduced a new scan check for
Why tagged?
- DAST from the title:
Making HTTP header injection critical with one promp
- DAST from the title:
Towards Effective Fuzzing of EDK2 Components
Securing bootloaders is critical to establishing the trusted computing base of modern systems. TianoCore's edk2, the de facto UEFI-based bootloader, is widely deployed but has recently been shown to contain numerous high-severity vulnerabilities. Existing approaches either…
Why tagged?
- SAST from the excerpt:
brid approach combining static analysis and Large Langu
- DAST from the excerpt:
automated technique for fuzzing edk2 protocols (i.e., b
- SAST from the excerpt:
DYNAS: A Dynamic Network Penetration Testing Framework Using Deep Hierarchical Reinforcement Learning
As network scale and uncertainty complicate automated penetration testing, reinforcement learning (RL) environments must support controlled evaluation under defensive and non-stationary conditions. We present DYNAS (Dynamic Network Attack Simulator), which combines…
Why tagged?
- DAST from the title:
YNAS: A Dynamic Network Penetration Testing Framework Using Deep
- DAST from the title:
Aikido launches external network pentesting
Aikido launches external network pentesting: AI agents attack your internet-facing systems from the outside and report only findings they actually exploit. Category: Company Updates
Why tagged?
- DAST from the title:
unches external network pentesting
- DAST from the title:
Adding Aikido AI pentesting to your existing security stack
Aikido Security's AI pentesting fits into the stack you already run. You can add AI pentesting on top to catch the complex logic flaws deterministic tools miss. Category: Guides & Best Practices
Why tagged?
- DAST from the title:
Adding Aikido AI pentesting to your existing sec
- DAST from the title:
Nuclei Templates releases Nuclei Templates v10.5.1 - Release Notes
New Templates Added: 68 | CVEs Added: 54 | First-time contributions: 11 🔥 Release Highlights 🔥 [CVE-2026-109618] PHP2Shell (CVE-2026-109618/CVE-2026-109619) - Active Crash Detection (@lcfr_hax, @assetnote, @princechaddha, @s4e-io) [critical] (vKEV) 🔥 [CVE-2026-105133]…
Why tagged?
- DAST from the title:
Nuclei Templates releases Nucl
- DAST from the title:
Typed Template Fuzzing
Fuzzing software with complex inputs has been a longstanding challenge. Traditionally, fuzzers either programmatically encode language constraints, requiring significant engineering effort, or rely on users to declare grammars and constraints. Recent LLM-based fuzzers address…
Why tagged?
- DAST from the excerpt:
Fuzzing software with complex i
- DAST from the excerpt:
JANUS: Agentic Cross-Language Fuzzing Harness Generation for Android Native Libraries
Modern Android apps extensively rely on native libraries, bridging Java/Kotlin and C/C++ through the Java Native Interface (JNI). This cross-language interoperation, however, exposes the memory-safe Android Runtime to the unsafe C/C++ world, creating an attack surface that has…
Why tagged?
- SAST from the excerpt:
API usage: (i) precise program analysis across the JNI boundary
- DAST from the title:
Agentic Cross-Language Fuzzing Harness Generation for
- SAST from the excerpt:
Raise or Check? Predicting the Necessity of Additional Fuzzing for Continuous Fuzzing
Continuous fuzzing is used for vulnerability detection in Open Source Software (OSS). Large-scale services such as Google's OSS-Fuzz fuzz over 1,300 projects and have revealed more than 10,000 vulnerabilities. Despite this, a considerable time lag often exists between when a…
Why tagged?
- SAST from the excerpt:
ous fuzzing is used for vulnerability detection in Open Source Software (OSS). Large-scale serv
- DAST from the excerpt:
Continuous fuzzing is used for vulnerabili
- SAST from the excerpt:
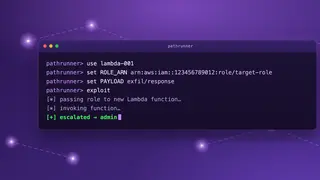
Introducing pathrunner: An AWS privilege escalation framework
Introducing pathrunner, a modular, cloud-native offensive security framework that automates the exploitation of AWS IAM privilege escalation paths.
Why tagged?
- DAST from the excerpt:
a modular, cloud-native offensive security framework that automate
- DAST from the excerpt:
Efficient Program Reduction for Library Fuzzing Harnesses
Library fuzzing harnesses translate generated inputs into API calls. When a complex harness triggers a crash, developers must determine whether the cause is a library defect or invalid harness usage. A smaller reproducer can simplify this investigation, but obtaining one…
Why tagged?
- DAST from the title:
m Reduction for Library Fuzzing Harnesses
- DAST from the title:
SolBehave: Evaluating the Behavioural Correctness of LLM-Generated Smart Contracts
Large language models increasingly generate Solidity smart contracts that, once deployed, can never be patched, making a single latent fault permanent and exploitable. Yet current evaluations mostly ask only whether generated code compiles. We introduce SolBehave, a benchmark…
Why tagged?
- DAST from the excerpt:
Differential fuzzing compares each generated
- Remediation from the excerpt:
deployed, can never be patched, making a single latent
- DAST from the excerpt:
Nuclei Templates releases Nuclei Templates v10.5.0 - Release Notes
New Templates Added: 295 | CVEs Added: 36 | First-time contributions: 11 🔥 Release Highlights 🔥 [CVE-2026-87902] WordPress Core - PHP Template Path Traversal (@Hadrian,FLX) [critical] (kev) (vKEV) 🔥 [CVE-2026-86218] N-able N-central <2026.3.1.14 - Pre-Authentication Remote…
Why tagged?
- DAST from the title:
Nuclei Templates releases Nucl
- DAST from the title:
HTTP/3 in Burp Suite - it’s time to find a bigger wordlist
How many bugs have you missed because you didn’t send quite enough HTTP requests? Turbo Intruder now supports HTTP/3, can comfortably exceed 100,000 requests per second over Wi-Fi, and auto-tunes for
Why tagged?
- DAST from the title:
HTTP/3 in Burp Suite - it’s time to fi
- DAST from the title:
SoK: From Finding to Deployment: Systematizing the OS Kernel Bug Lifecycle
Automated kernel bug discovery has advanced rapidly. Continuous fuzzing and static analysis systems, such as syzbot, now expose Linux kernel bugs at a scale that downstream processes struggle to absorb. Yet a crash report is only the beginning. Before a bug is eliminated, it…
Why tagged?
- SAST from the excerpt:
Continuous fuzzing and static analysis systems, such as syzbot
- DAST from the excerpt:
Continuous fuzzing and static analysis sys
- Remediation from the excerpt:
be triaged, understood, patched, validated, reviewed, i
- SAST from the excerpt:
Nuclei Templates releases Nuclei Templates v10.4.9 - Release Notes
New Templates Added: 123 | CVEs Added: 85 | First-time contributions: 15 🔥 Release Highlights 🔥 [CVE-2026-86207] N-able N-central - Authentication Bypass (@rapid7, @DhiyaneshDk) [critical] (vKEV) 🔥 [CVE-2026-85706] GitLab CE/EE <=19.1.7/19.2.5/19.3.1 - Arbitrary File Read…
Why tagged?
- DAST from the title:
Nuclei Templates releases Nucl
- DAST from the title:
Why Your AI Application Is Exposed (Even When Your Scans Come Back Clean)
AI applications can pass security scans yet remain exploitable through chained attacks across models, tools, data, and business workflows. Learn how DAST, AI pentesting, and red teaming work together to expose end-to-end risk.
Why tagged?
- DAST from the excerpt:
ss workflows. Learn how DAST, AI pentesting, and red
- DAST from the excerpt:
Nuclei Templates releases Nuclei Templates v10.4.8 - Release Notes
New Templates Added: 112 | CVEs Added: 101 | First-time contributions: 22 🔥 Release Highlights 🔥 [CVE-2026-72898] Metabase - Unauthenticated SQL Injection (@0x_Akoko, @pdteam) [critical] (kev) (vKEV) 🔥 [CVE-2026-71362] Adobe Commerce/Magento - Customer Session Identity…
Why tagged?
- DAST from the title:
Nuclei Templates releases Nucl
- DAST from the title:
Show, Don't Tell: What Evo Continuous Offensive Security Found in a Real Enterprise SaaS
A real Evo Continuous Offensive Security assessment uncovered 33 confirmed vulnerabilities in a multi-tenant enterprise SaaS, including tenant-wide compromise and critical authorization flaws.
Why tagged?
- DAST from the title:
ll: What Evo Continuous Offensive Security Found in a Real Enterpr
- DAST from the title:
ZAP Updates - July 2026
ZAP was started more than 13 million times in July, another big jump, and the Client Spider officially became our recommended option for crawling modern web apps.
Why tagged?
- DAST from the excerpt:
recommended option for crawling modern web apps.
- DAST from the excerpt:
CRLF-Powered Desync Attacks: Beheading HTTP Streams
Found Header Injection? Make it a critical with one prompt Has the scanner reported HTTP request header injection? Try asking Burp AT to exploit the issue with our CRLF-Powered Desync and Tunnelling s
Why tagged?
- DAST from the title:
CRLF-Powered Desync Attacks: Beheading HTTP Stream
- DAST from the title:
Continuous Offensive Security & AI Pentesting: 20 FAQs
Get answers to 20 common questions about continuous offensive security, AI penetration testing, DAST, and AI red teaming.
Why tagged?
- DAST from the title:
Offensive Security & AI Pentesting: 20 FAQs
- DAST from the title:
Evo Continuous Offensive Security Is Here Pentesting Grade Coverage For The 350 Days A Year You Aren't Testing
Snyk Evo Continuous Offensive Security brings autonomous, AI-powered pentesting to the 350 days between traditional tests, uncovering exploitable flaws attackers can find first.
Why tagged?
- DAST from the title:
ensive Security Is Here Pentesting Grade Coverage For T
- DAST from the title:
Nuclei Templates releases Nuclei Templates v10.4.7 - Release Notes
New Templates Added: 122 | CVEs Added: 49 | First-time contributions: 23 🔥 Release Highlights 🔥 [CVE-2026-63030] WordPress Core 6.9-7.0.1 - Pre-Auth Batch-Route Confusion (@slcyber, @mielverkerken, @pdteam, @flx-0x00) [critical] (kev) (vKEV) 🔥 [CVE-2026-60004] Gitea <=…
Why tagged?
- DAST from the title:
Nuclei Templates releases Nucl
- DAST from the title:







End of list · 44 developments in the last 120 days